Services
Full time
DevSecOps Platform Specialist (Senior)
Cybersecurity · Quebec City or Montreal · Hybrid
You’re the person who builds the security tool and uses it. Instead of launching a scan, exporting a 400-finding PDF and wishing the devs good luck, you sort out what’s real, you set aside the false positives and you show the team how to fix the rest. Half of your time, you do application security on Vooban’s projects. The other half, you develop the security platform we’re building in-house: you see a finding we still triage by hand, you automate it; you see a blurry trust boundary, you model it and close it. You work hand in hand with our devs and the cyber team, not from an ivory tower.
The platform brings together in one place threat modeling, a security graph, system composition analysis, vulnerability triage and compliance tracking, with AI agents that do a good part of the analysis in the background. Nobody is going to hand you a neatly wrapped ticket: you take ownership of a feature, from the data model to the interface, and you decide how to secure it. It’s an environment made for people who prefer proving that a control works rather than claiming that it exists. And it’s a rare role, where full-stack, security, platform and applied AI often intersect in the same merge request.
Pssst: we mostly work remotely, but you must be able to come by our Quebec City or Montreal offices when needed.
Here's a list of the main softwares and languages we use. You don't need to be familiar with them all, don't worry!
Claude
Claude Code
Typescript
React
Postgresql
Kubernetes
LLM
Here at Vooban, we take care of our own. That’s why we have put everything in place to create a welcoming and stimulating work environment where innovation overflows. Our employees’ well-being is paramount, and we do everything in our power to offer extraordinary benefits and an incredible atmosphere. Join us to see what we have in store for you!
We're growing fast with three offices ready to welcome you. Whether you're in Quebec City, Montreal, or Toronto, you have the freedom to choose your workplace, at the office or from home. But we make sure the office vibe is so great, you'll actually want to be there.
You can choose between 35, 37.5 or 40-hour weeks. What’s more, each hour of overtime will be paid!
Each month, you receive an allowance to cover your public transportation or parking. Whether it's your bus pass, metro pass, BIXI or À Vélo membership, it's reimbursable up to the eligible amount. If you're based in Quebec City, you can also choose to use our indoor parking.
We have plenty of coffee, tea, beer, fruit, and snacks (and it’s free!) And if cooking’s not your thing, you can always order lunches delivered straight to the office.
Taking care of our own is one of our core values. That’s why our vibrant Social Club organizes a variety of activities. On top of that, we have our many happy hours, our renowned recognition gala, and our must-attend summer and holiday parties.
As you can see, we love variety: golf tournaments, lively happy hours, tailgates, pub crawls, pilates, yoga, and so much more. And the best part? It’s all on Vooban!
Each team has a monthly budget to carry out team building activities.
From smoothie making to cake tasting, we always finds a way to cheer us up!
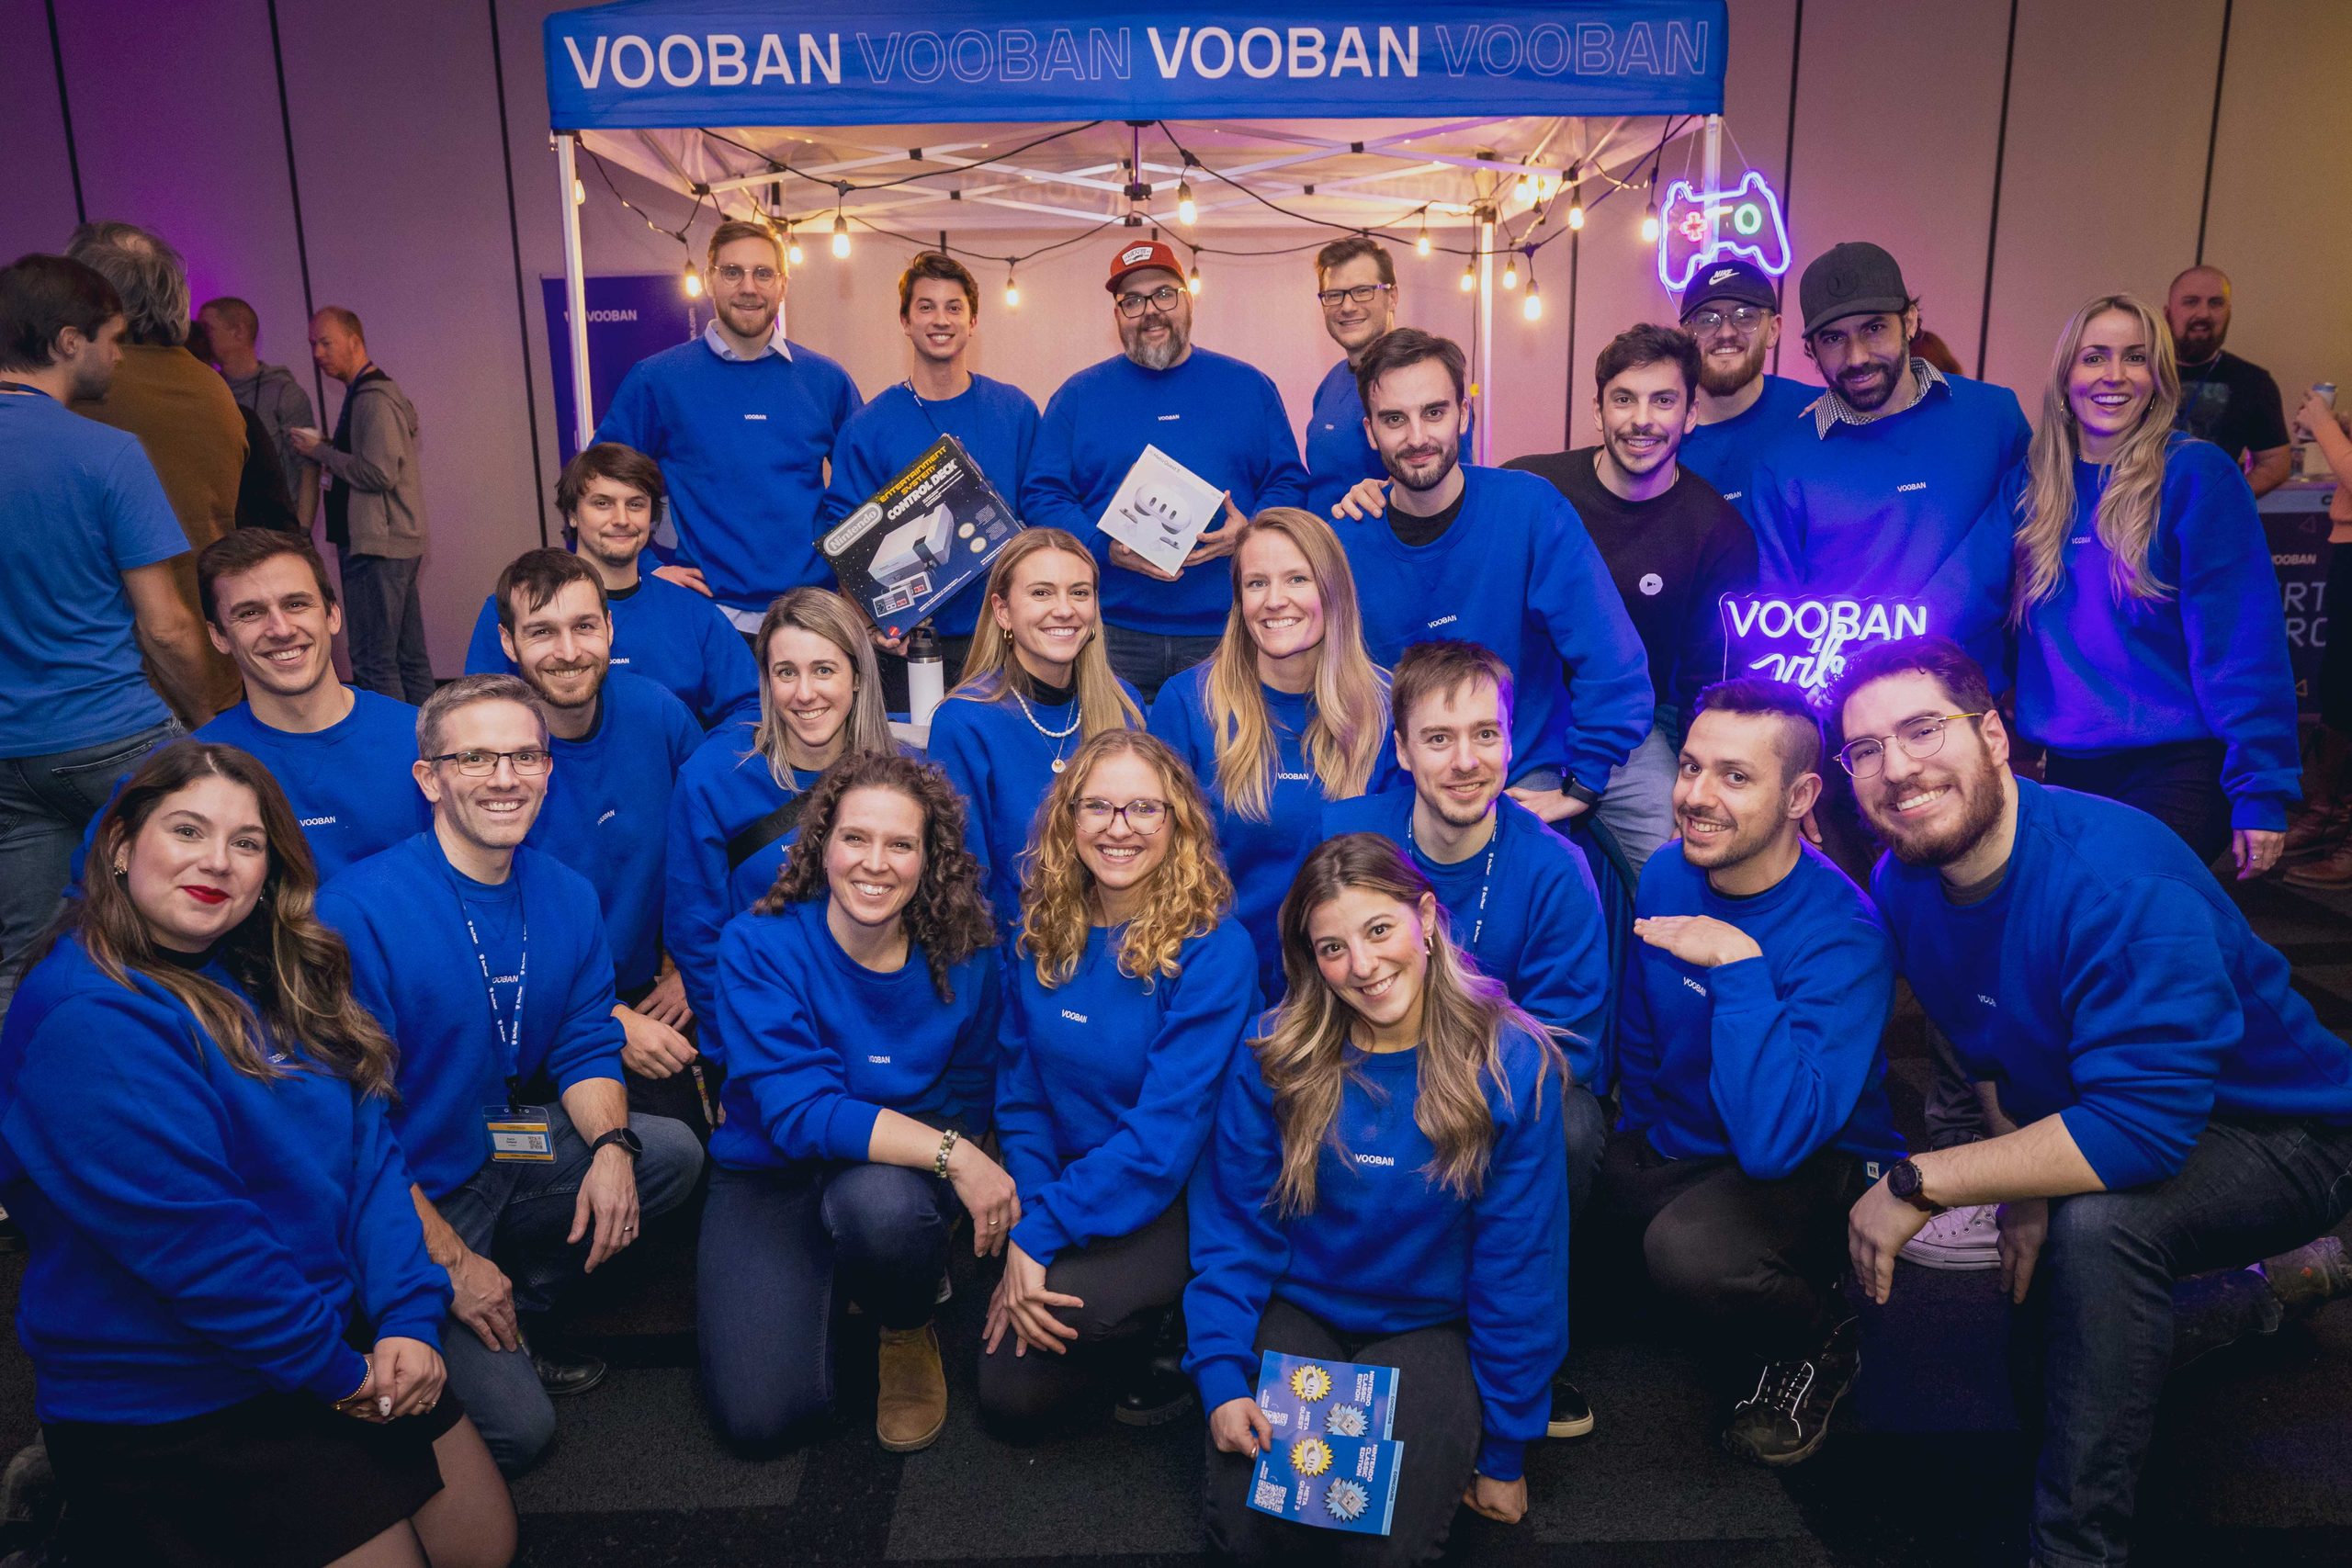
We’re so tightly woven that we almost think of calling each other in the morning to dress the same!
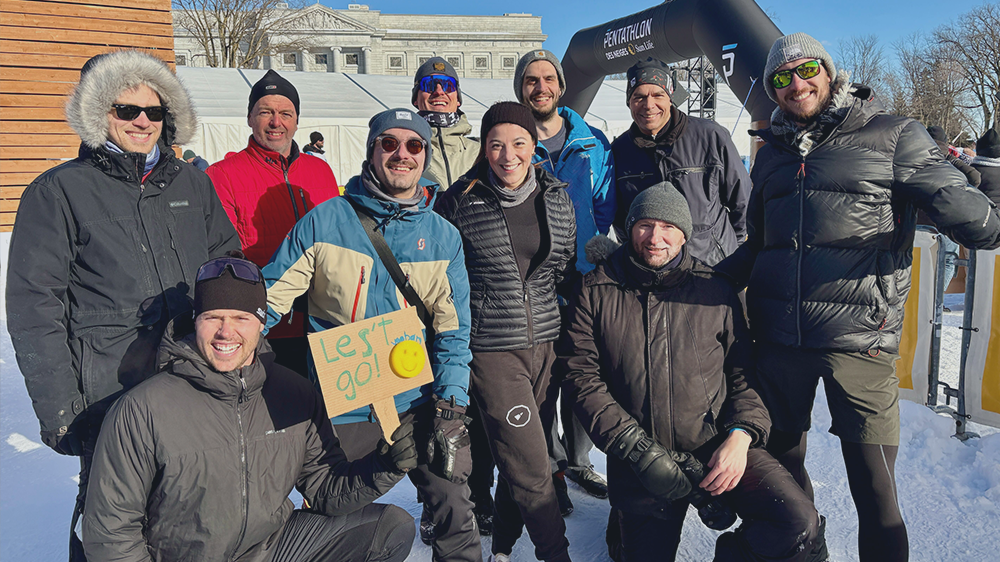
Every year, we get together for the Snow Pentathlon and give it our all in five sports: running, cross-country skiing, skating, snowshoeing, and running.
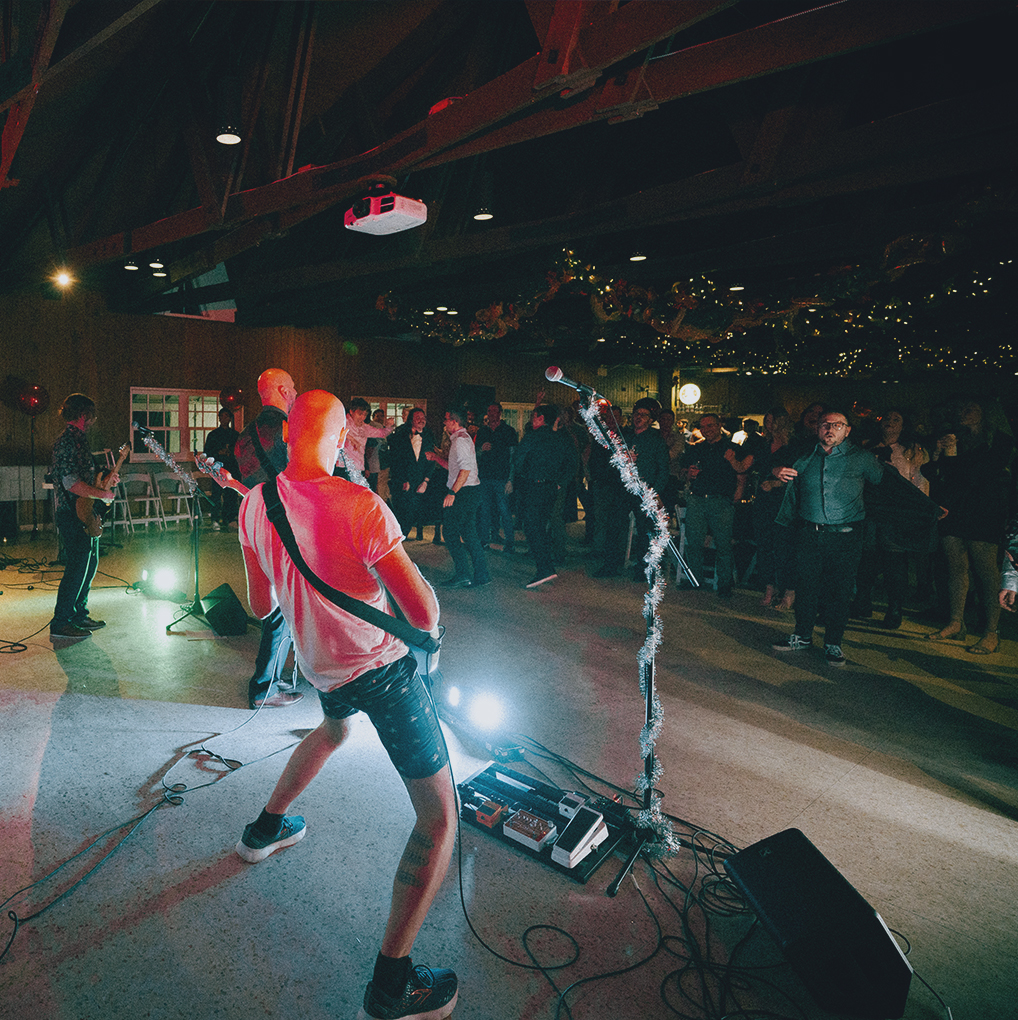
What could be more memorable than our live Vooban show at festive events like Christmas parties?
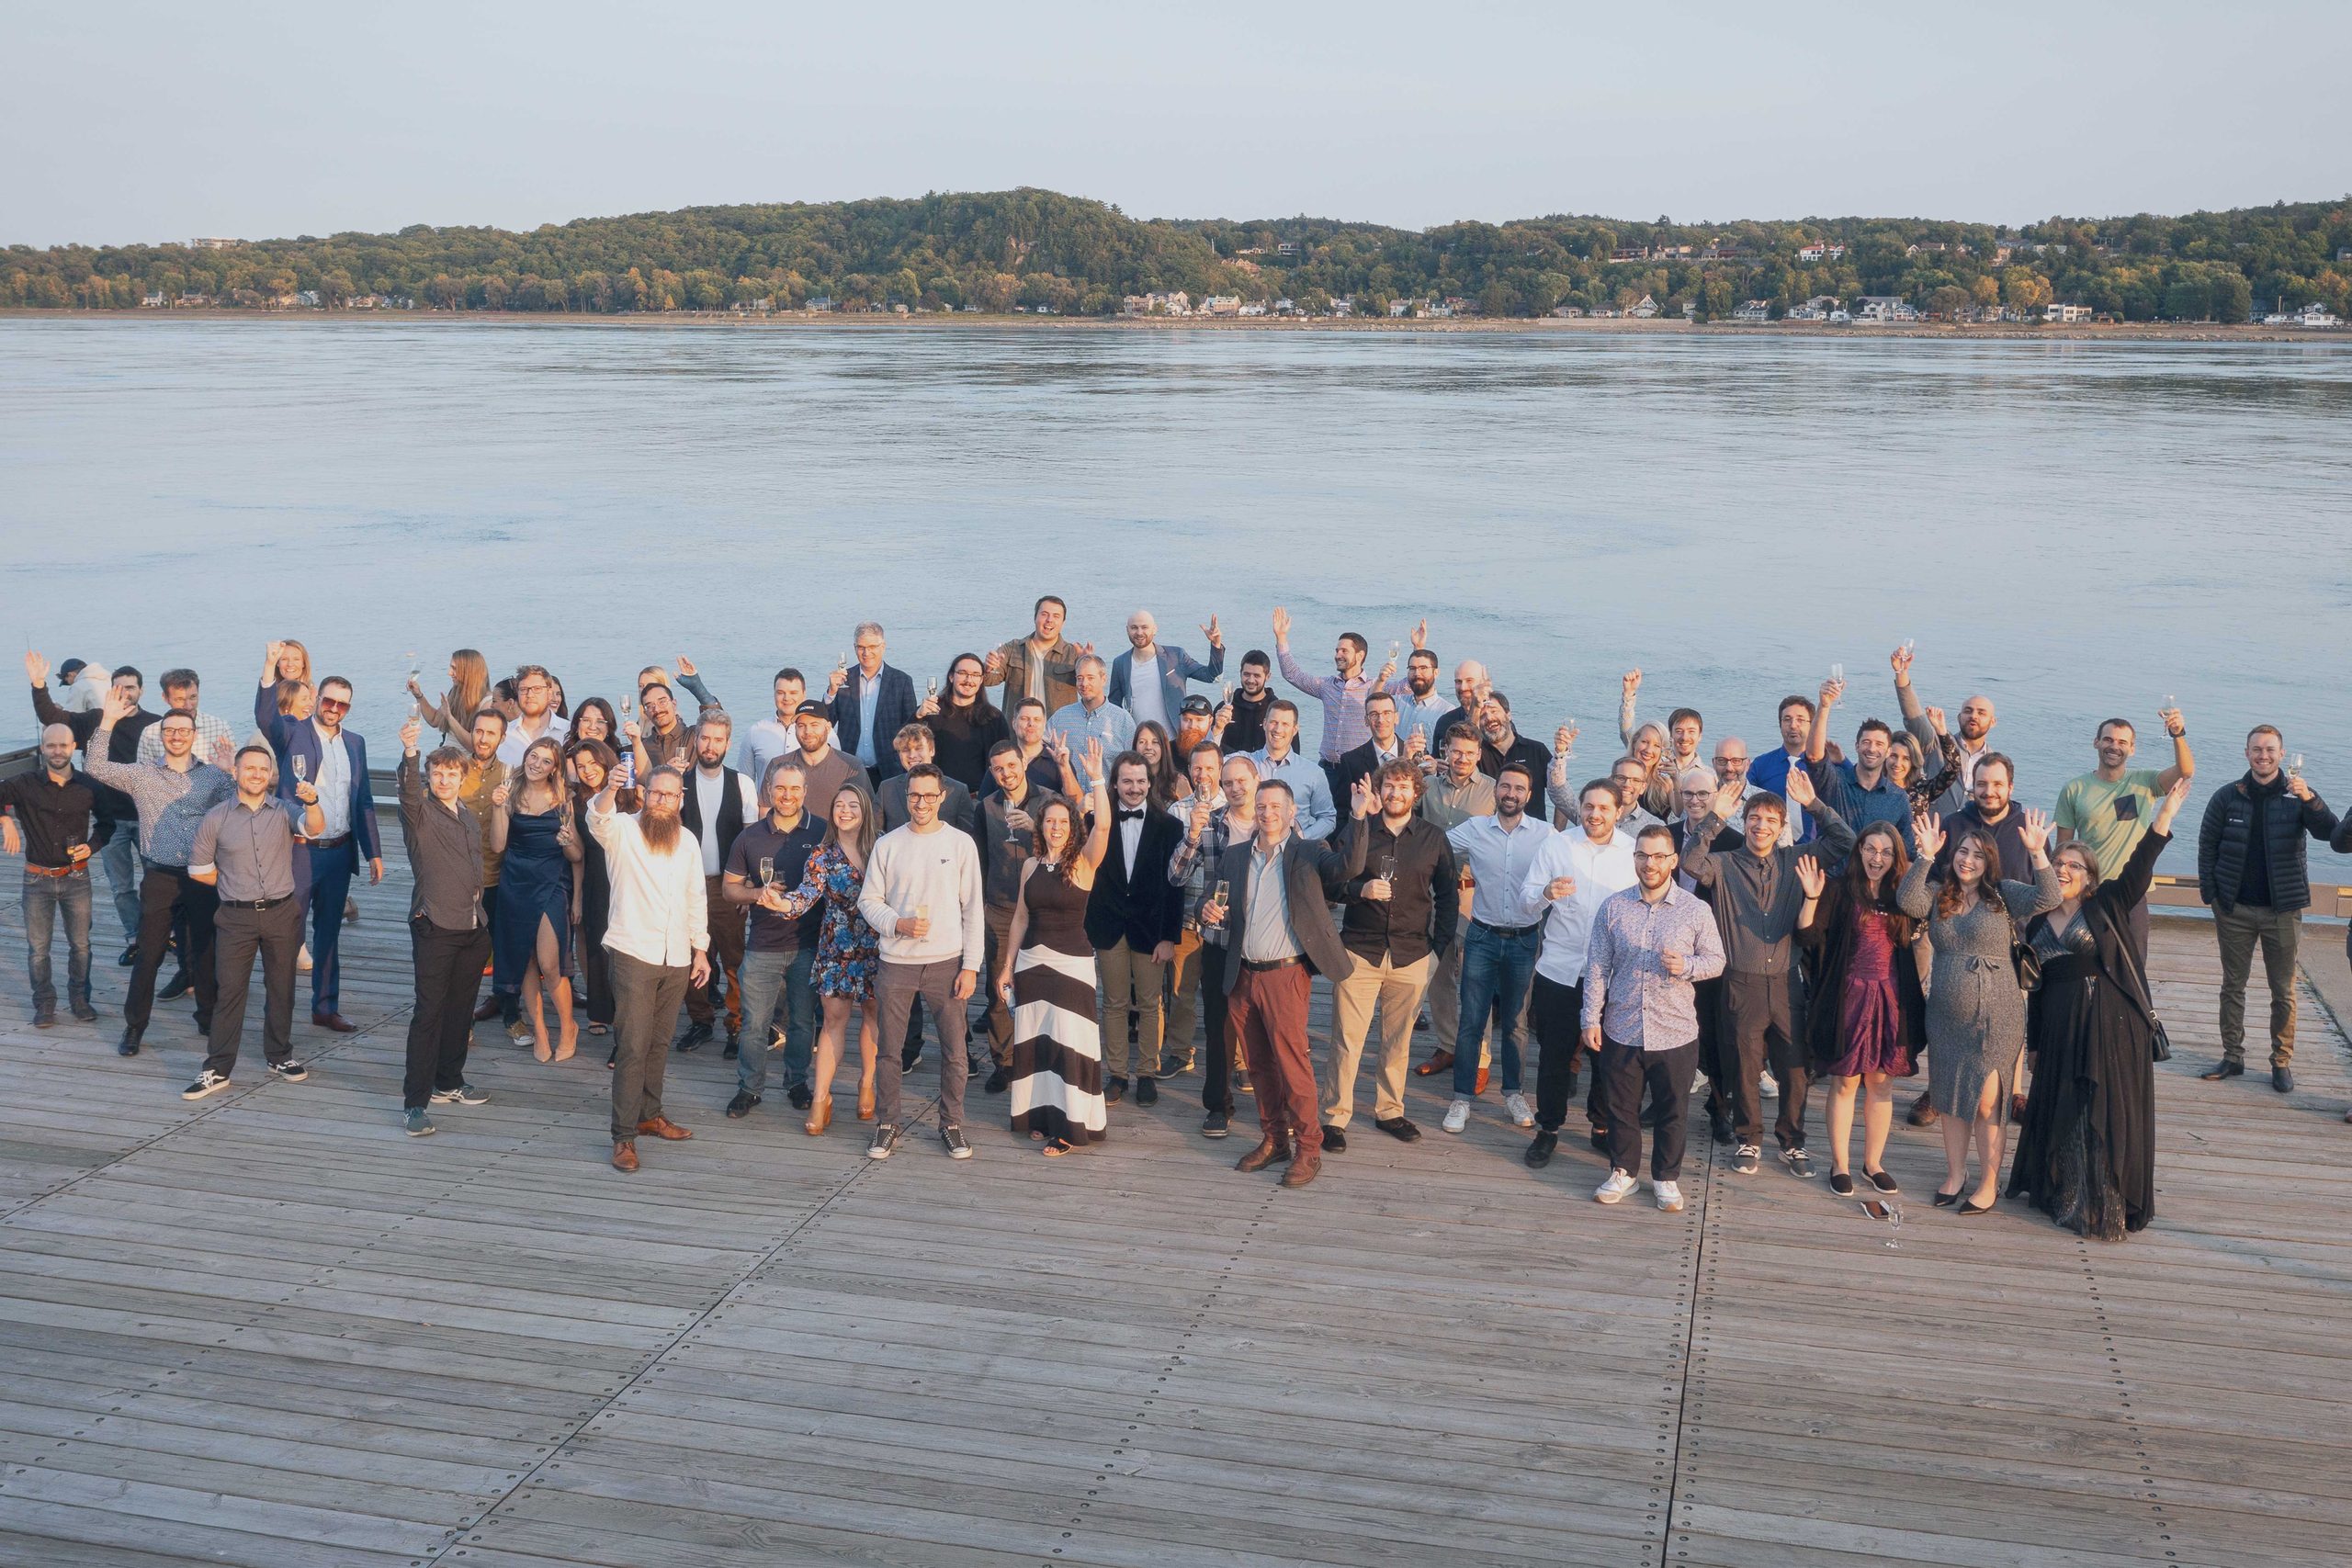
Our famous appreciation gala is a fun-filled event where we celebrate the team’s achievements and efforts, making it a highlight of our calendar!
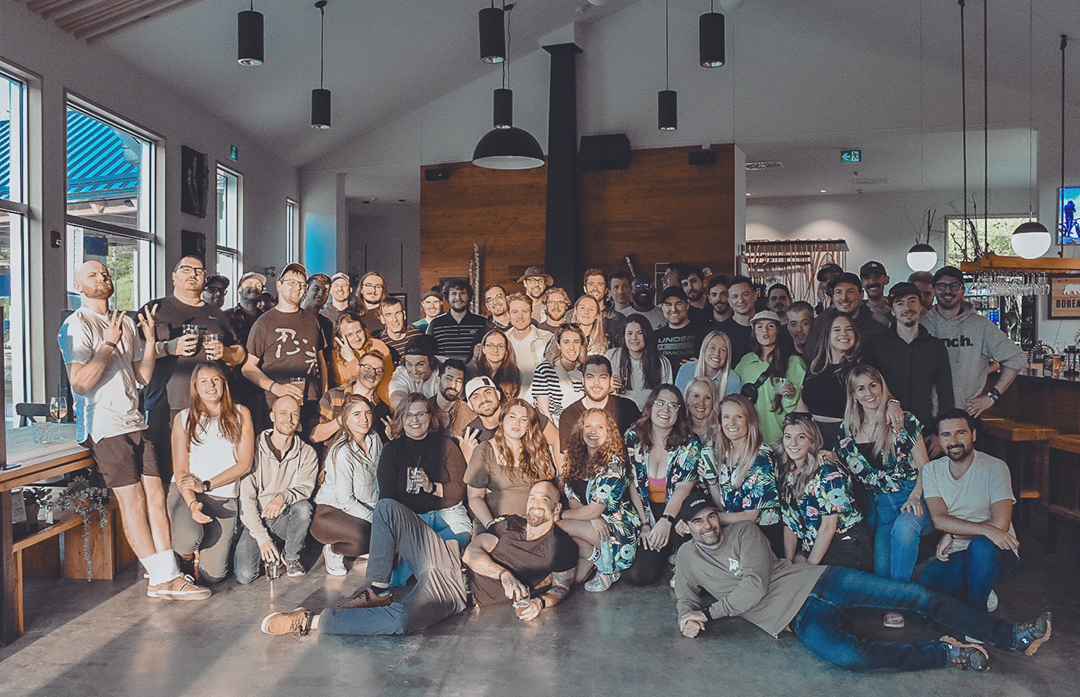
It is, without a doubt, our most epic event of the year. It includes barbecue, the Vooband, our very own Olympics, and some good old karaoke!
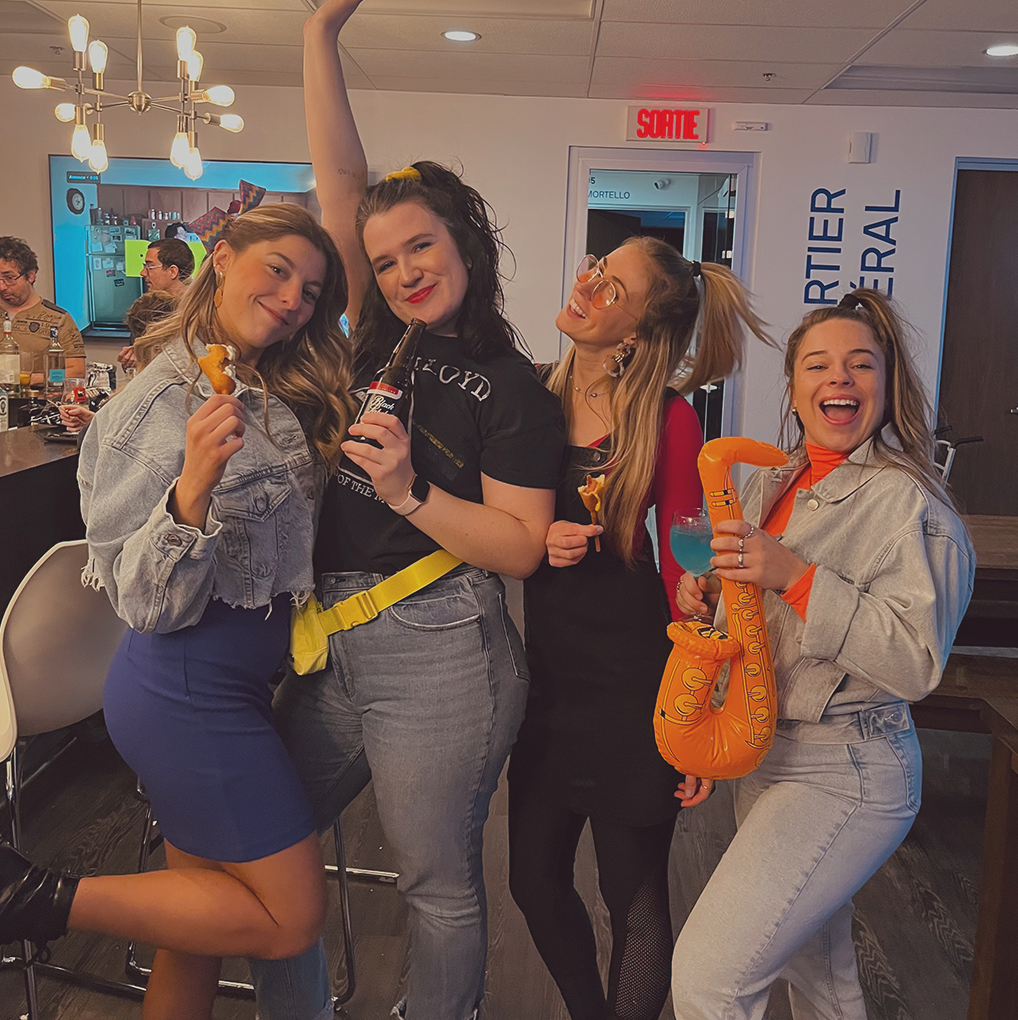
A new tradition is born at Vooban: awarding the famous Yearbook! This collection brings together the « best of » past years, memorable photos, and, above all, the best inside jokes of the year!
Whether you wish to gain new career skills or move to Hawaii when you retire, we help you make those dreams come true!
We offer a group RRSP to which Vooban contributes up to 4% of your salary, up to $4,000 per year.
Every employee has access to a training program tailored to their needs and receives a $2,500 bonus upon earning their certification.
Do you have a cause close to your heart? Perfect! Our ESG committee manages a budget dedicated to donations to support causes and organizations that matter to us. And if you’re interested, you can even join the committee!
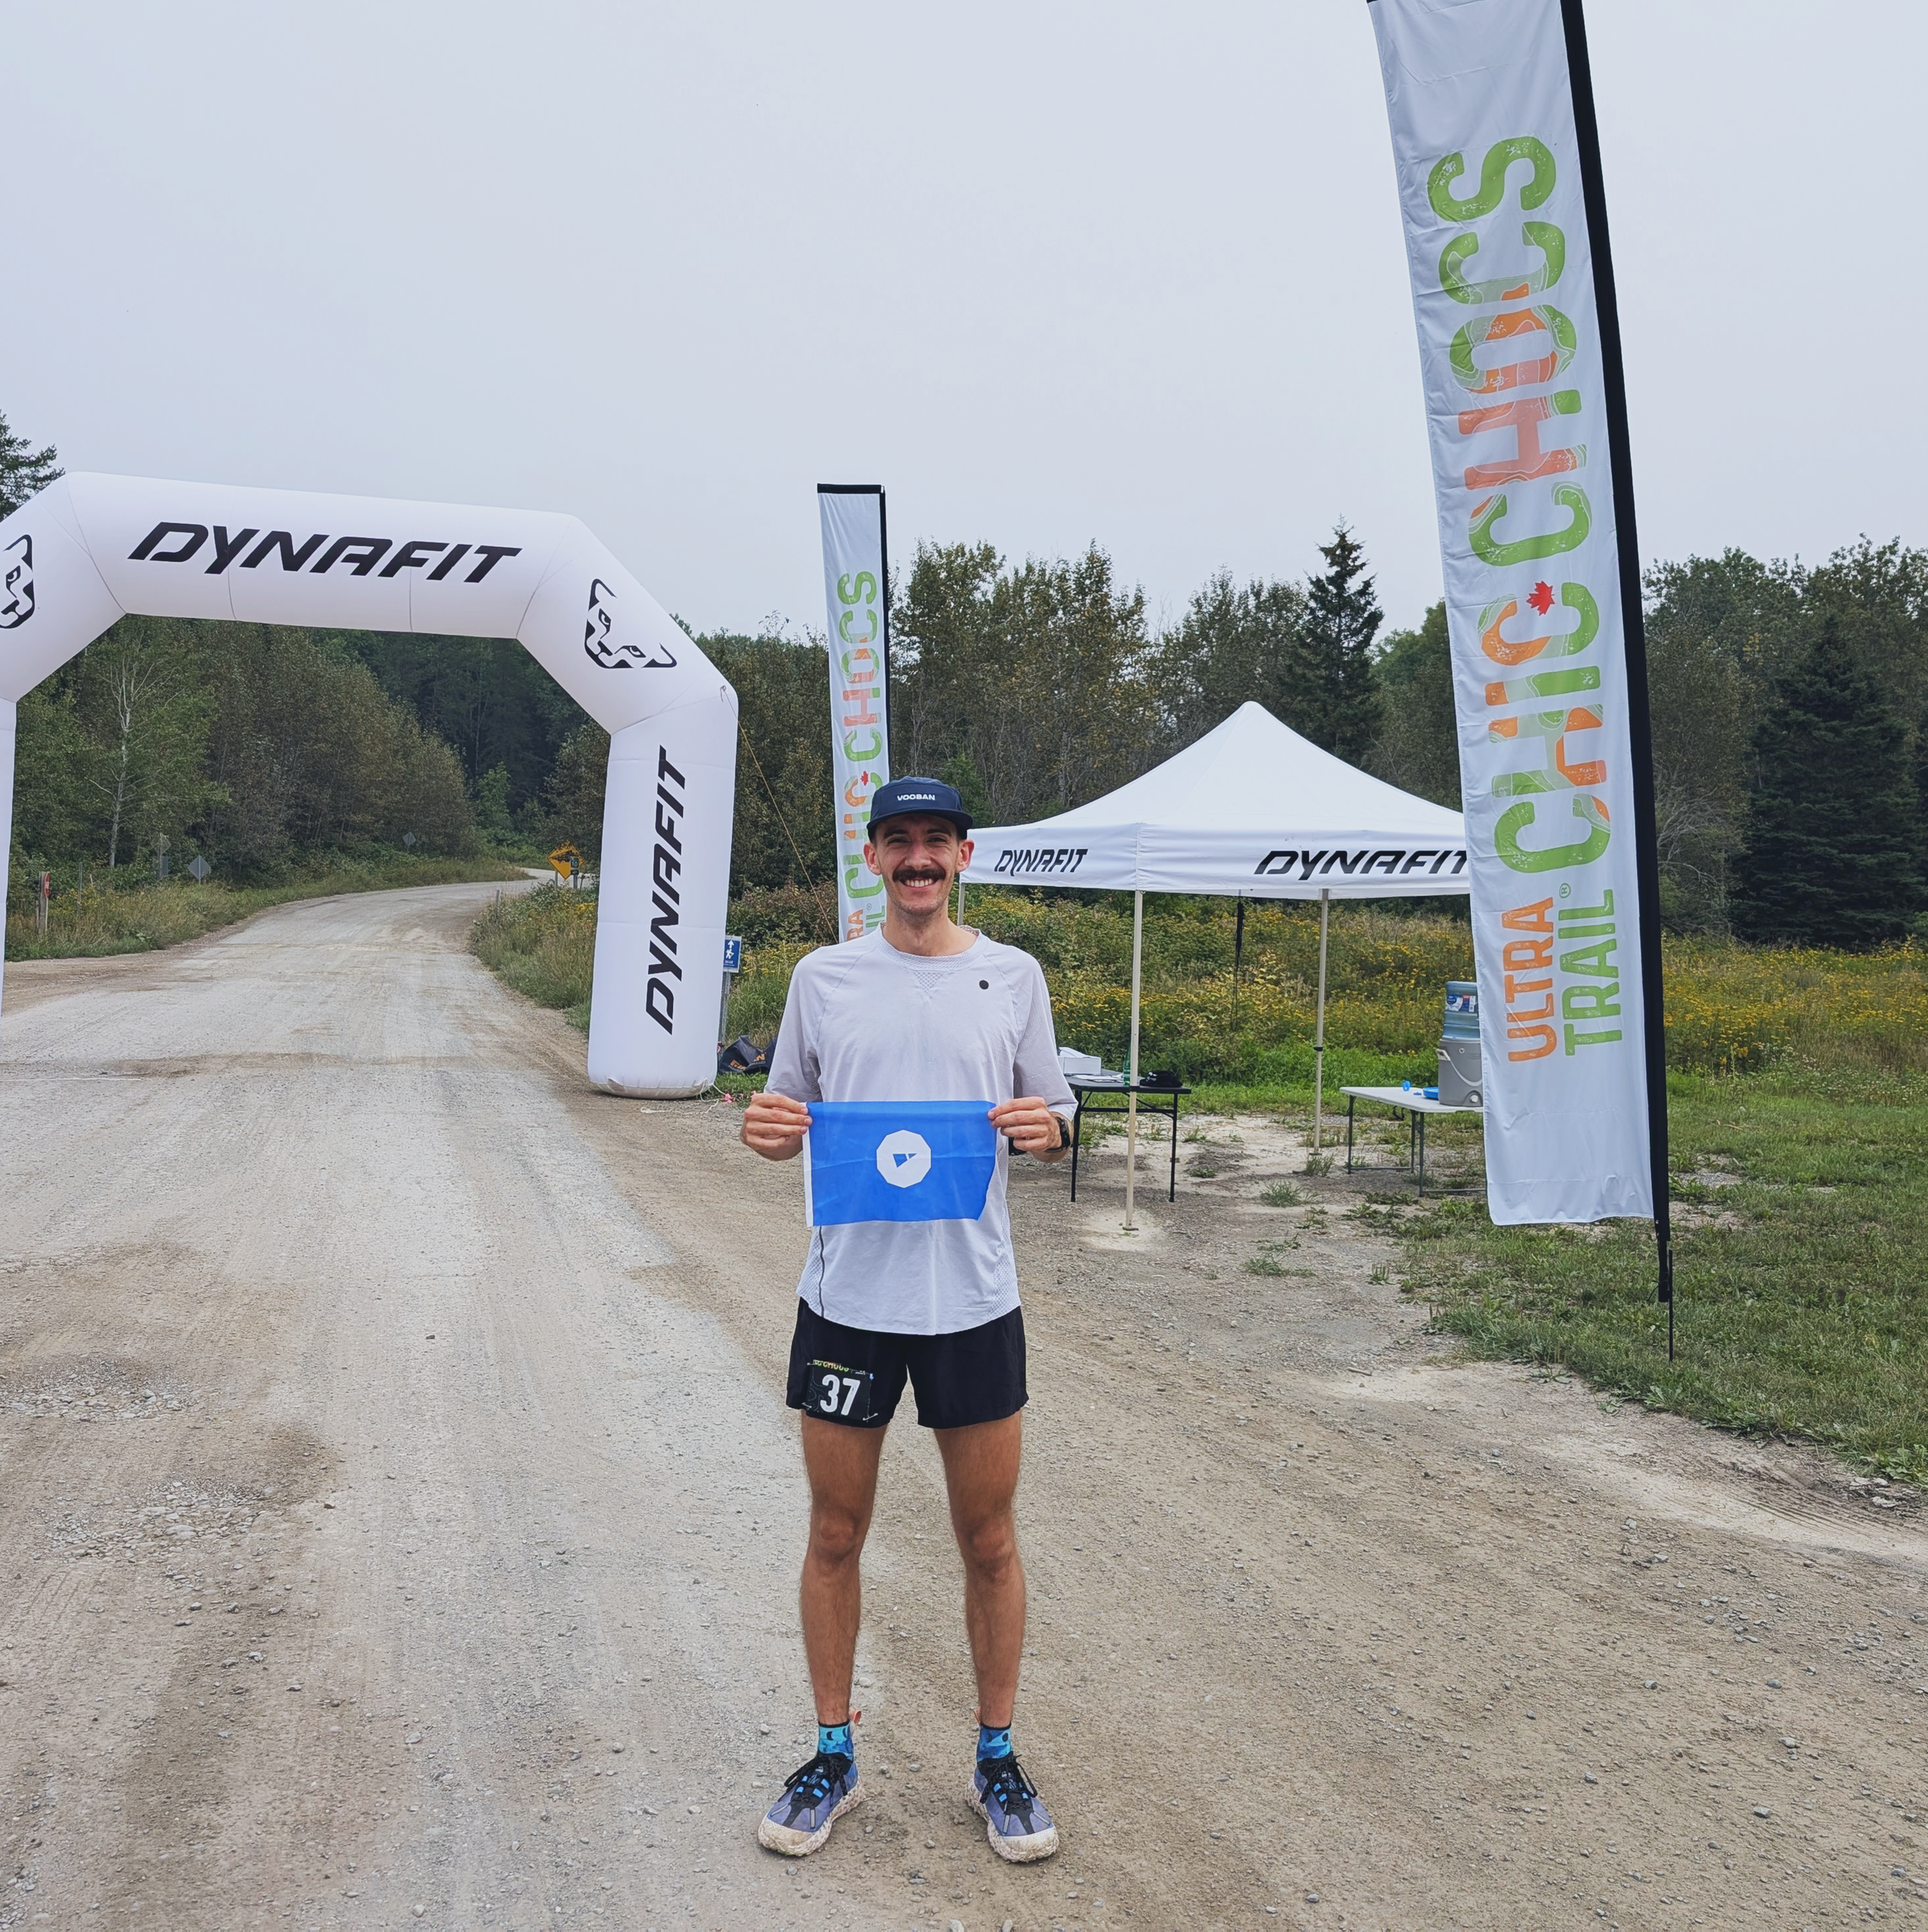
Our ESG committee also aims to encourage the remarkable achievements of our employees, like Robin's trail challenge: 172 km of running known to be extremely challenging! Bring on the challenges!
Here at Vooban, we make your mental and physical health our top priority. That’s why we give you access to lots of physical activities and healthcare professionals.
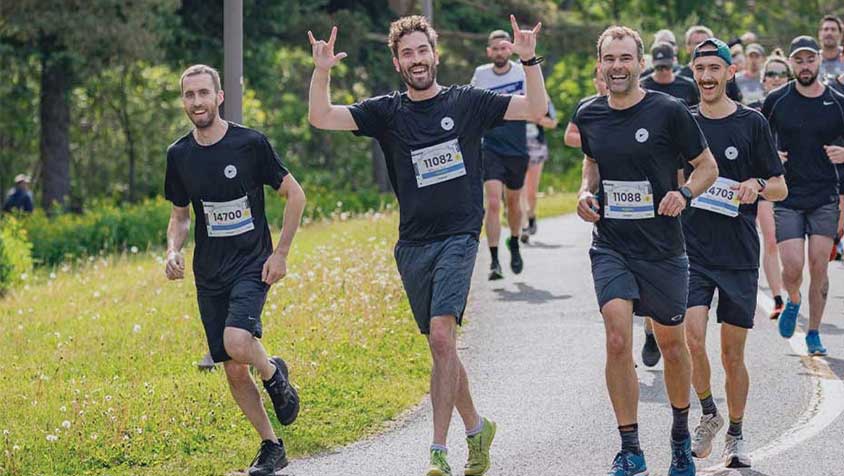
Every year, you get a $500 allowance to help you stay active. Plus, sports activities like spinning, boxing, and even tennis are organized every month!
Your individual health plan is paid in totality by Vooban!
You get access to the Telus Health telemedicine platform so you can consult a doctor online whenever needed.
We have an employee assistance program (EAP) which lets you benefit from a multitude of services for free: legal advice, psychologists, nutritionists, etc.
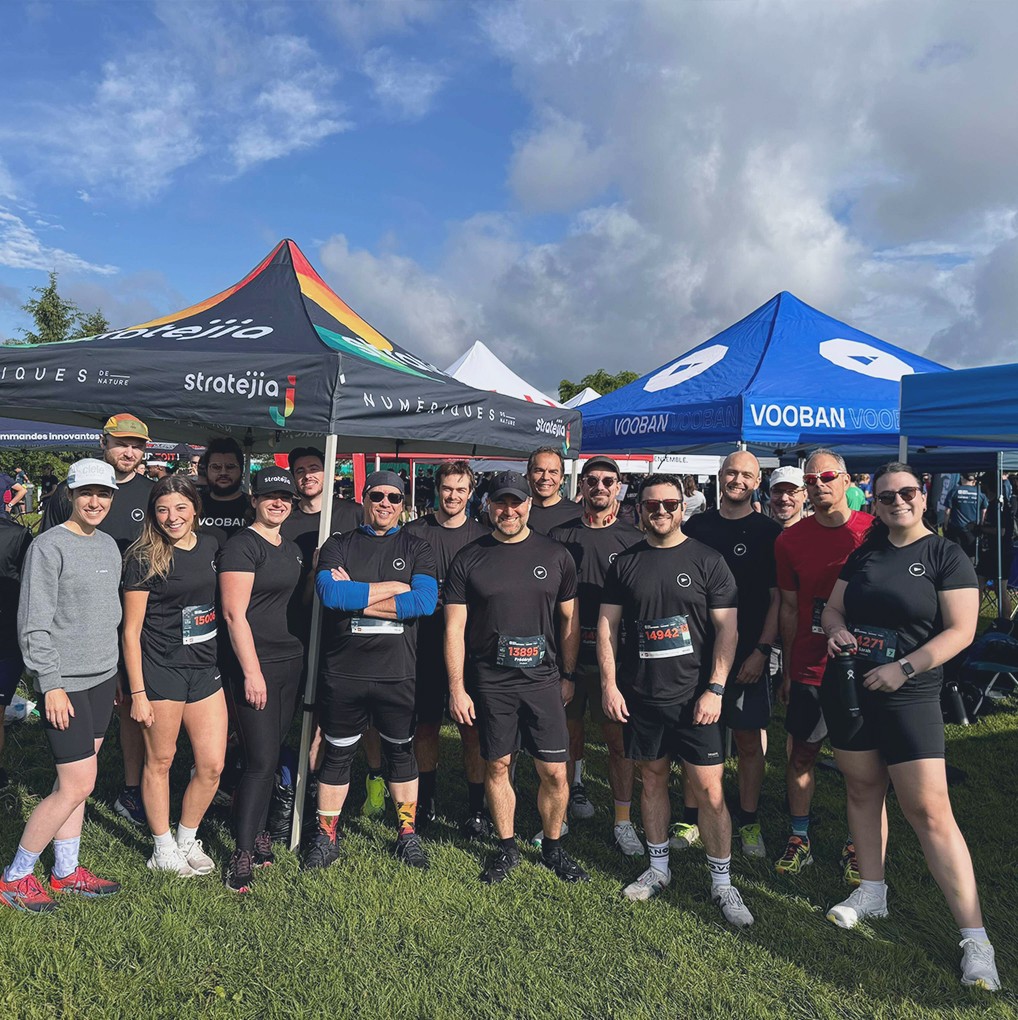
Whether you’re a marathon runner or more of a Sunday runner, every year, we sign up for the Business Challenge to push ourselves and, above all, have a lot of fun together.
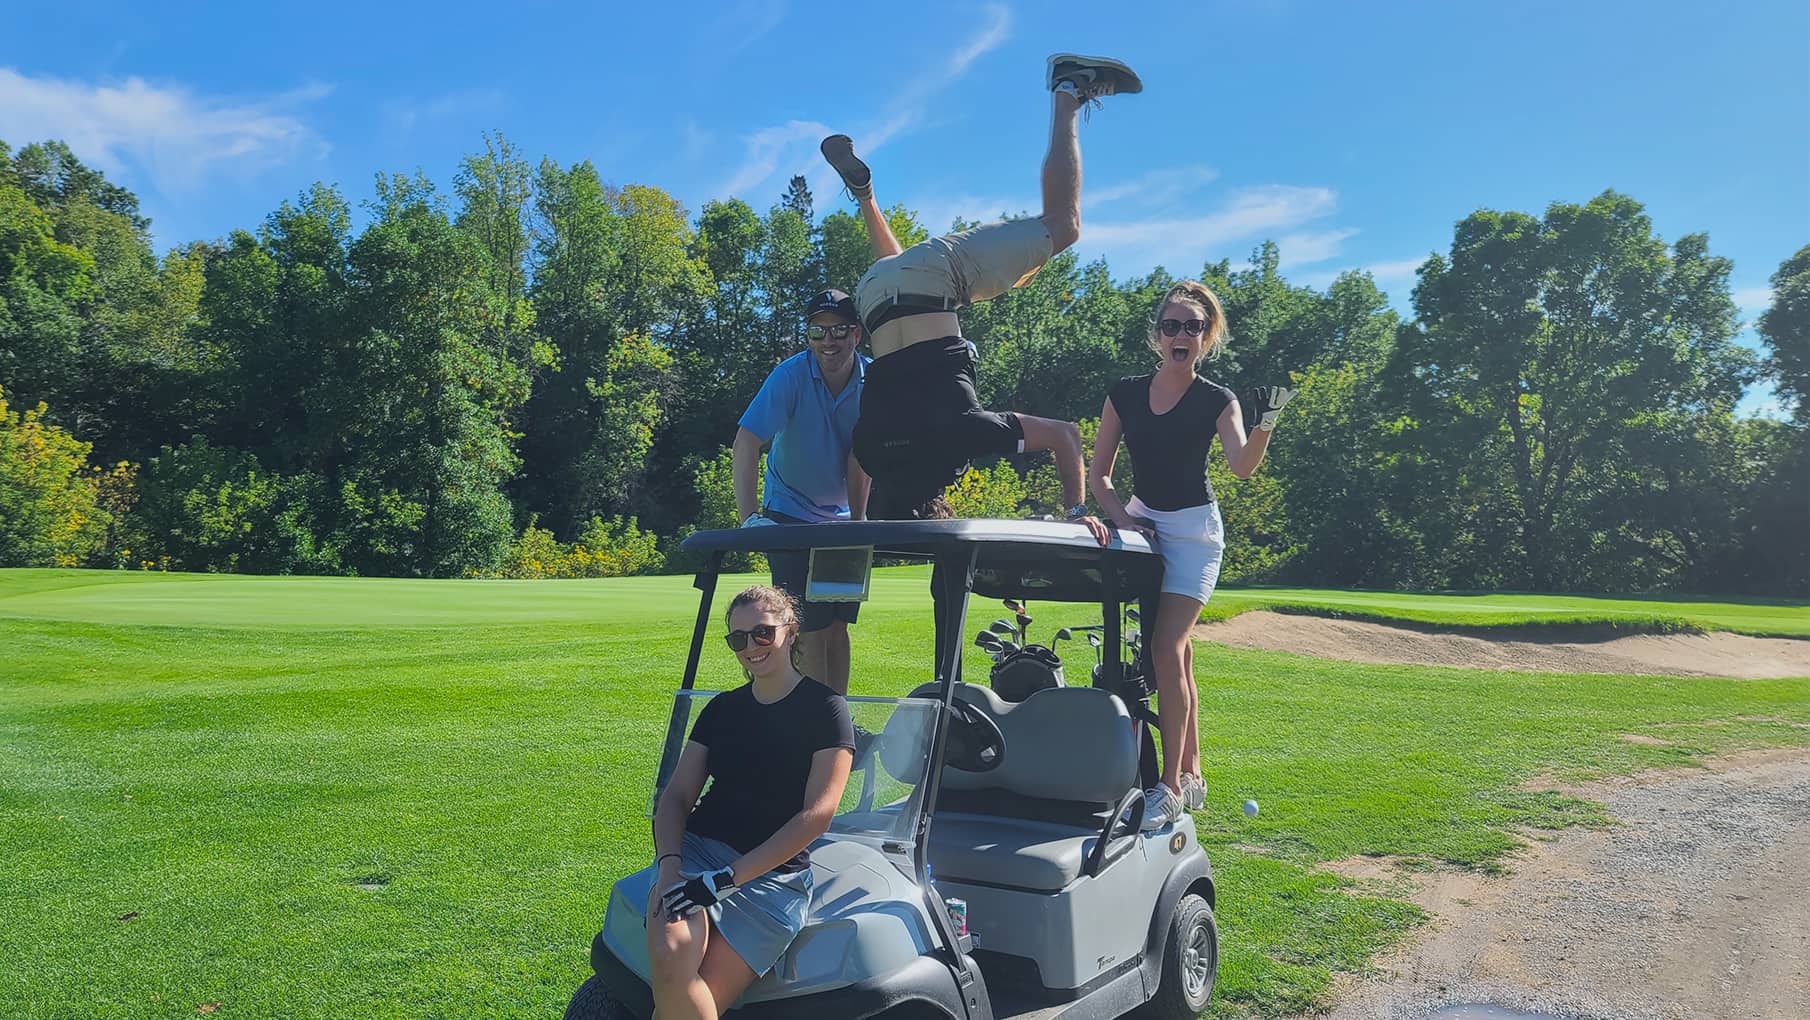
Every year, we host a golf tournament in which a prestigious trophy is at stake. P.S. Special acknowledgement to David for the gymnastics.
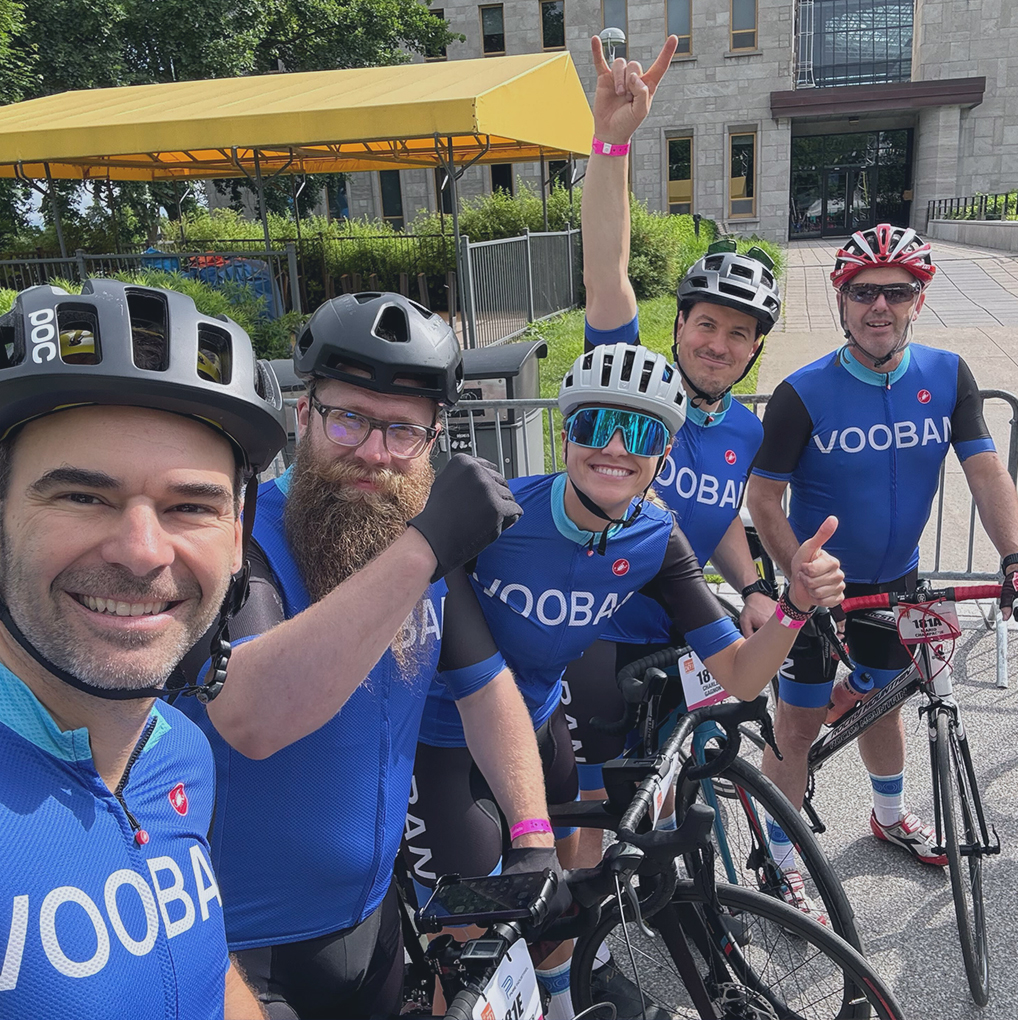
CHALLENGE WON! Vooban took part in the Grand défi Pierre Lavoie 2024 for the first time! It’s fair to say we’re all pumped up to ride as much as 1000 kilometers. There’s nothing more powerful than that to bond a team!
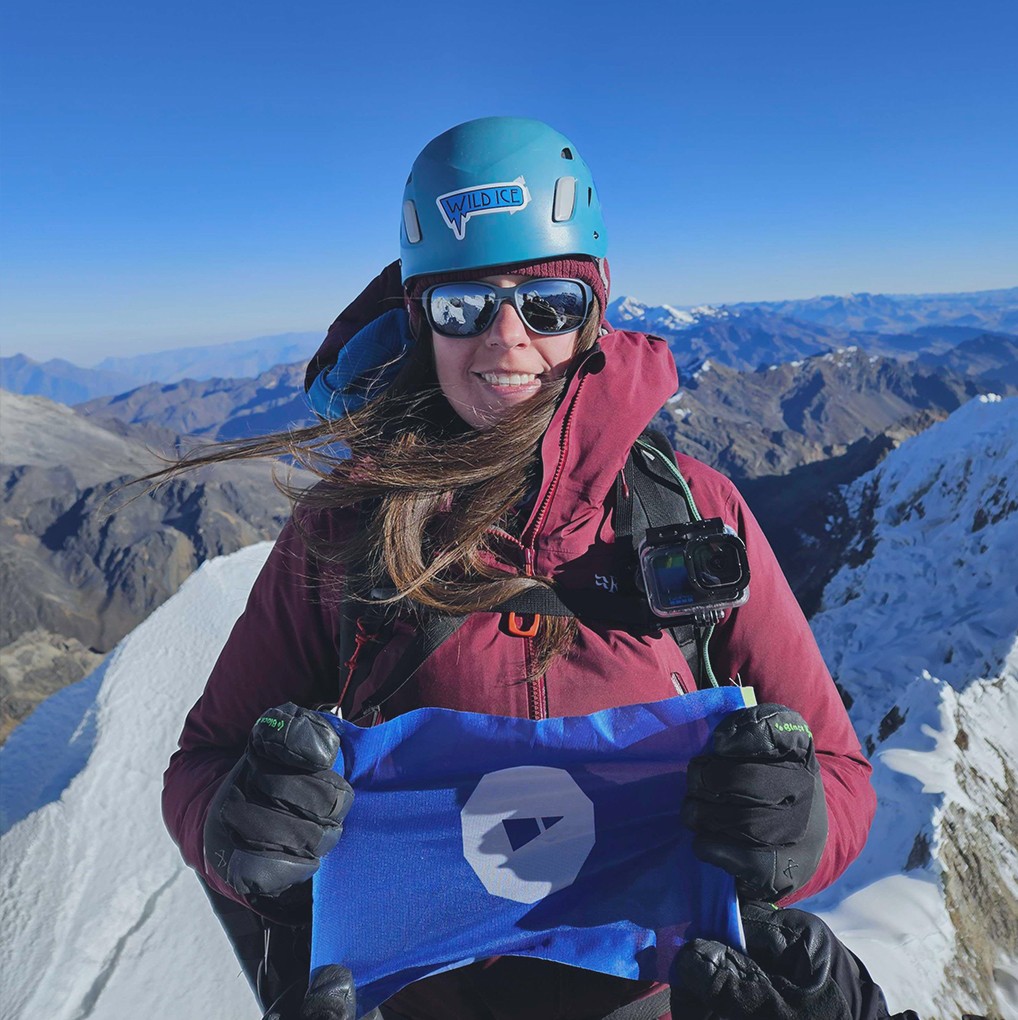
We’re proud to support employees with a bit between their teeth, like Audrey, who climbed to the top of the 5947-metre-high Alpamayo!
As soon as you arrive, we provide you with all the equipment needed to settle in at home or at the office. Plus, you won’t have to worry about your work attire thanks to our very own Vooshop!
We make sure you have nothing but the best: latest generation MacBook Pro, two 24-inch 4k screens and an adjustable ergonomic table.
On your first day, we give you $500 to buy what you’re missing (keyboard, mouse, footrest, etc.) and a gift card so you can get plenty of gear on the Vooshop (clothing, thermos, sport bag, etc.)
You have $120 a month to pay for your cellphone and internet plan.
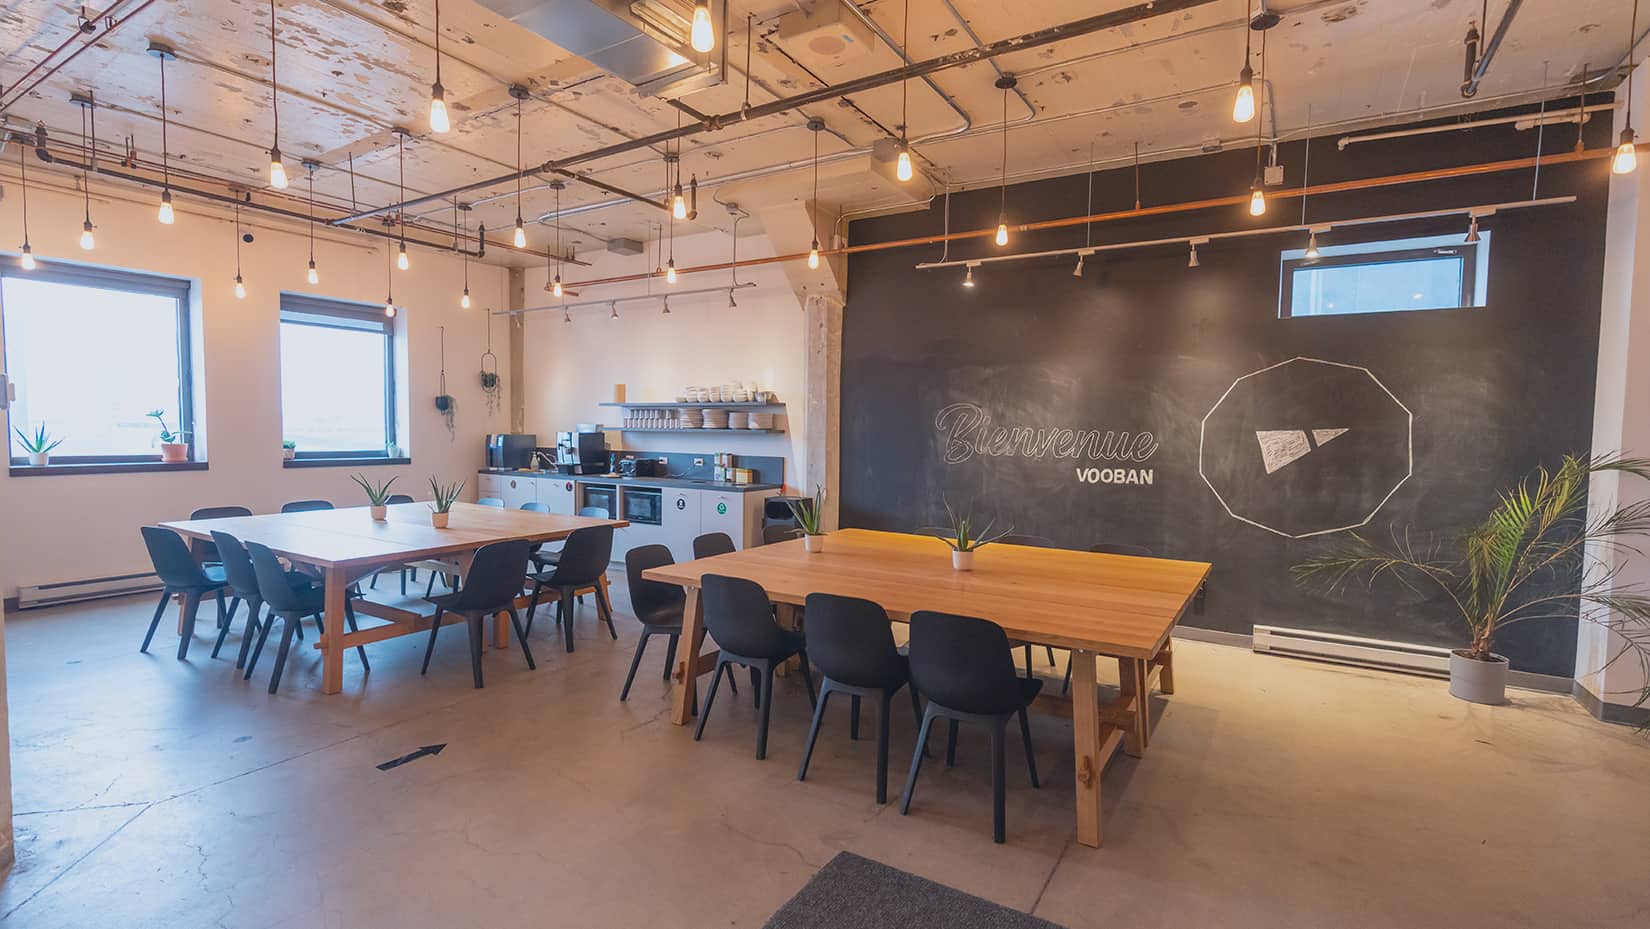
Our Montreal office is located directly in Quartier des Spectacles and near Place des arts, which means we are in the center of the action! It's also easily accessible via several Metro lines.
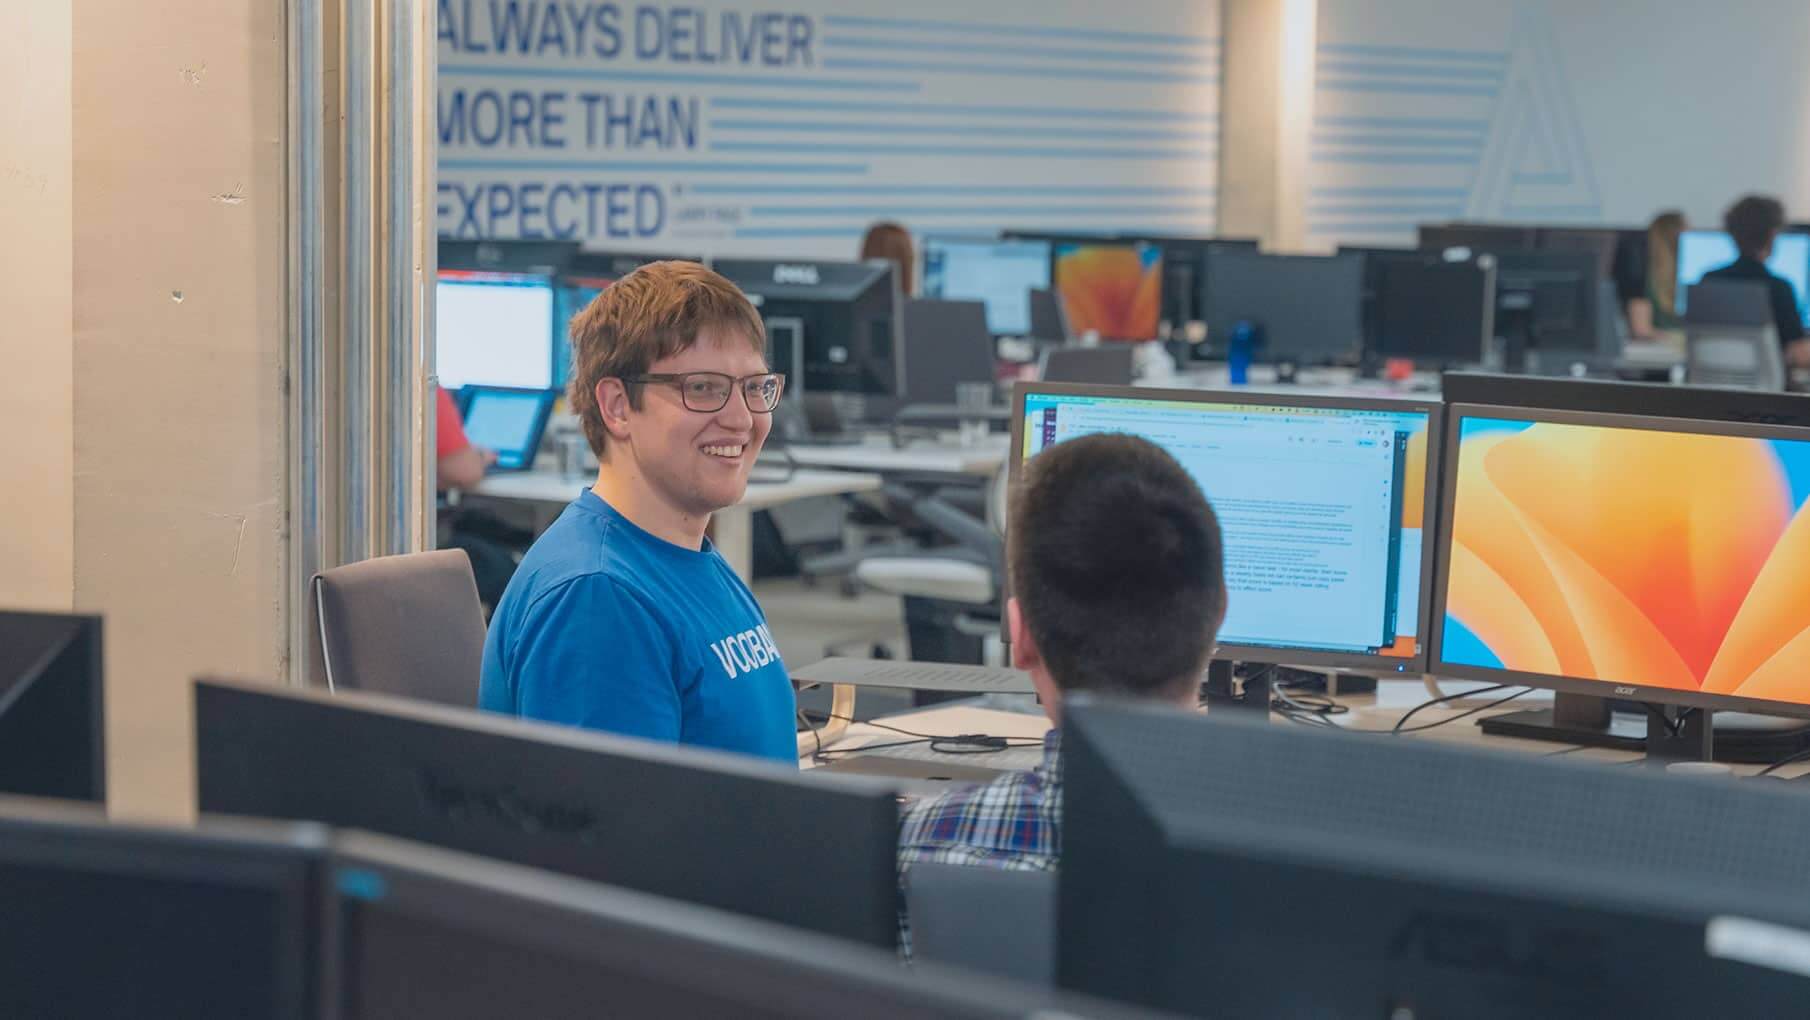
Our new open-plan offices with a modern industrial look are the perfect place for creative exchanges!
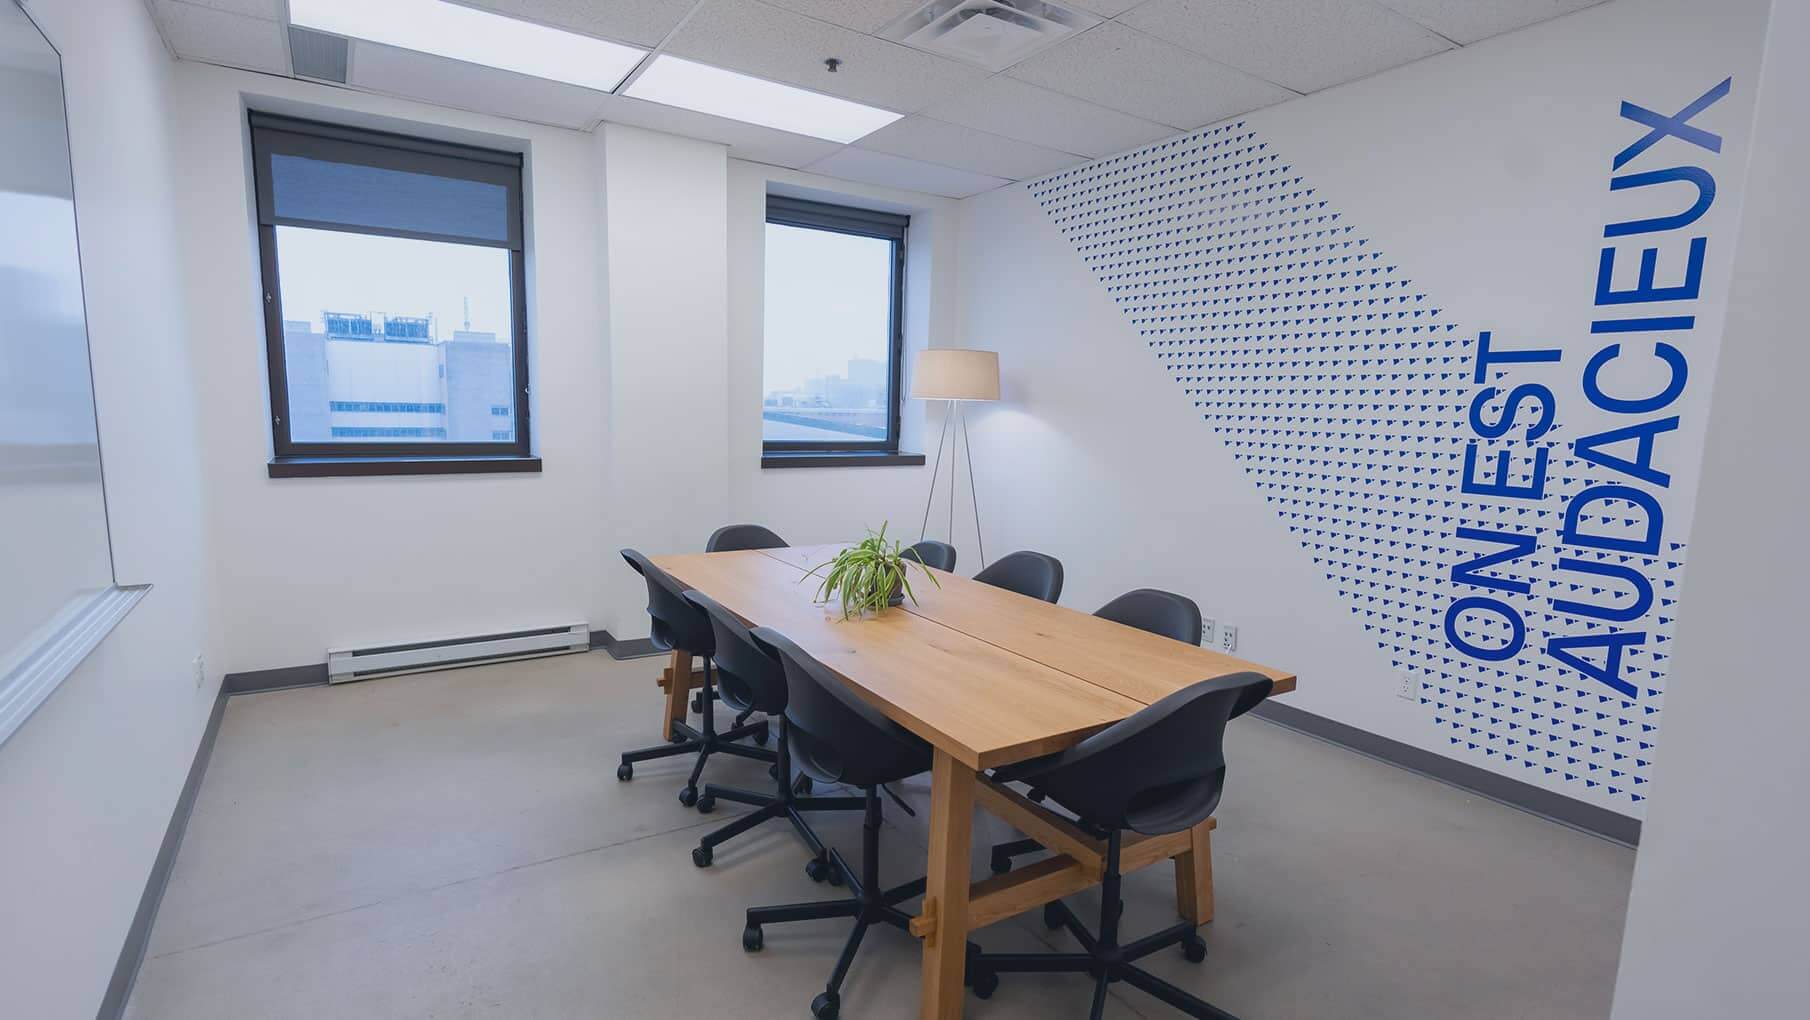
Named in honor of different Montreal neighborhoods, nine different conference rooms are accessible at all times for group meetings or simply for a little more peace and quiet.
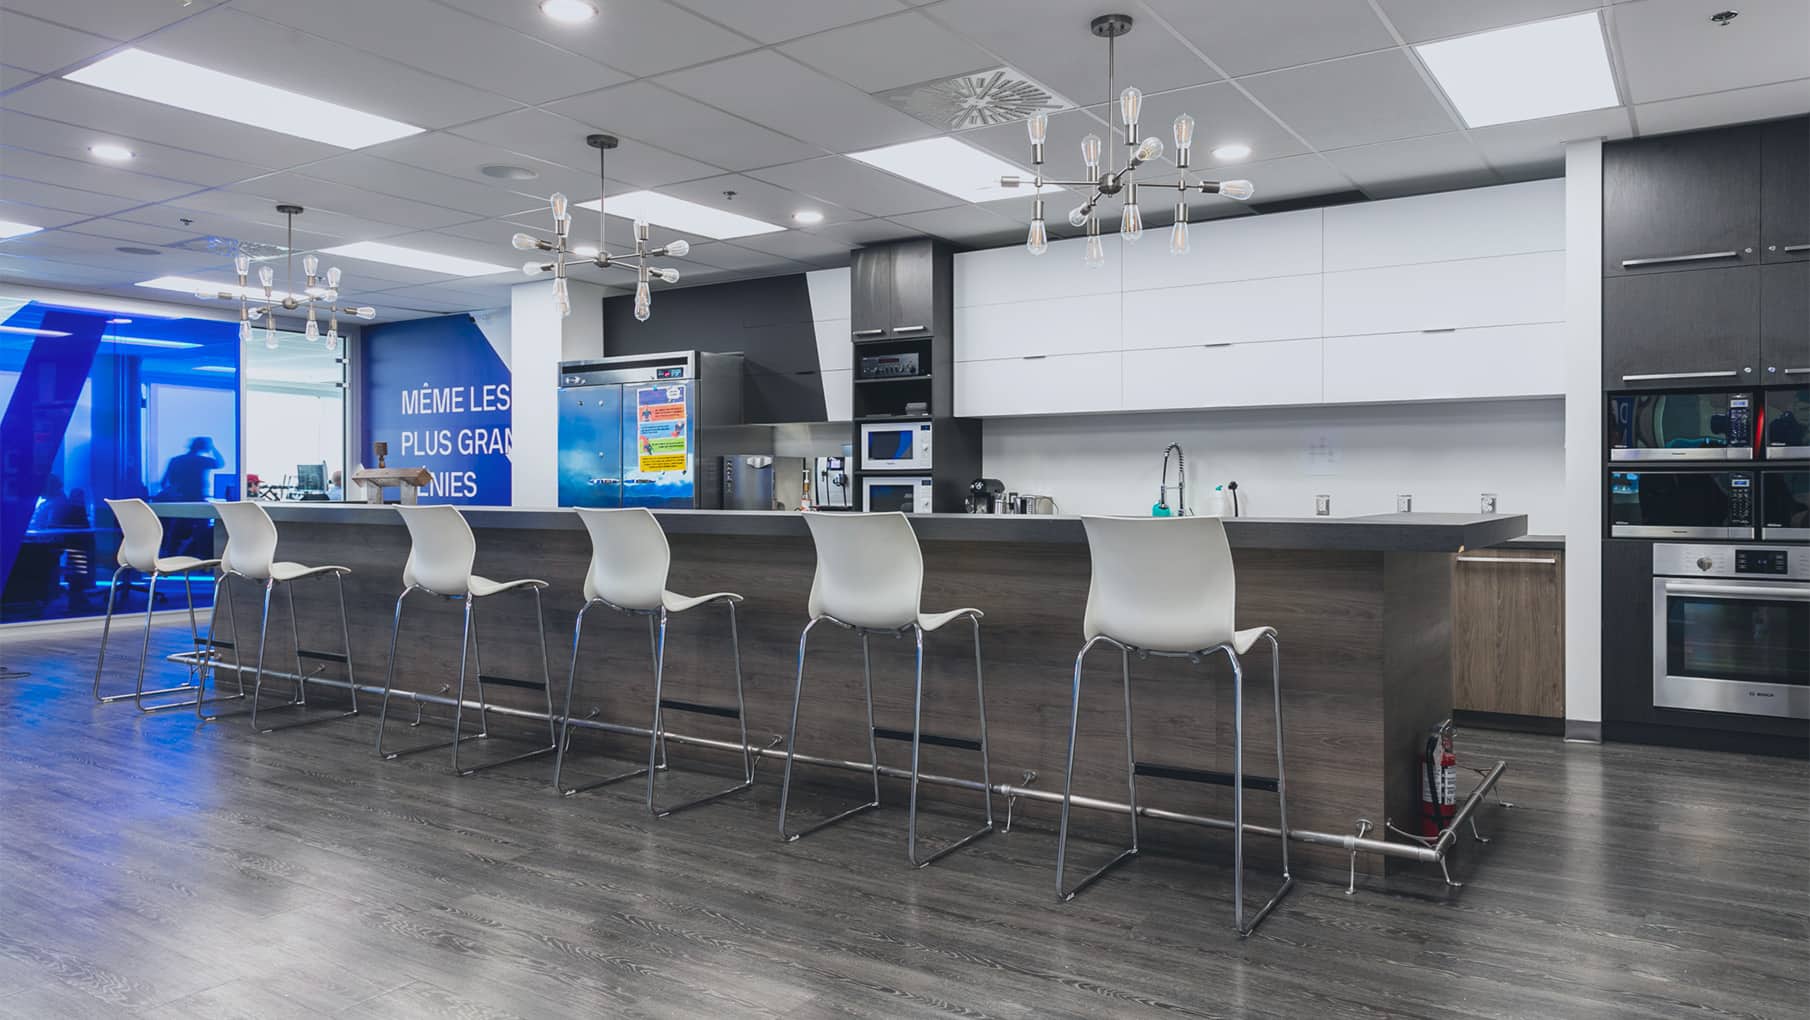
More than a simple lunchroom, The Headquarters is the #1 gathering place for all our happy hours.
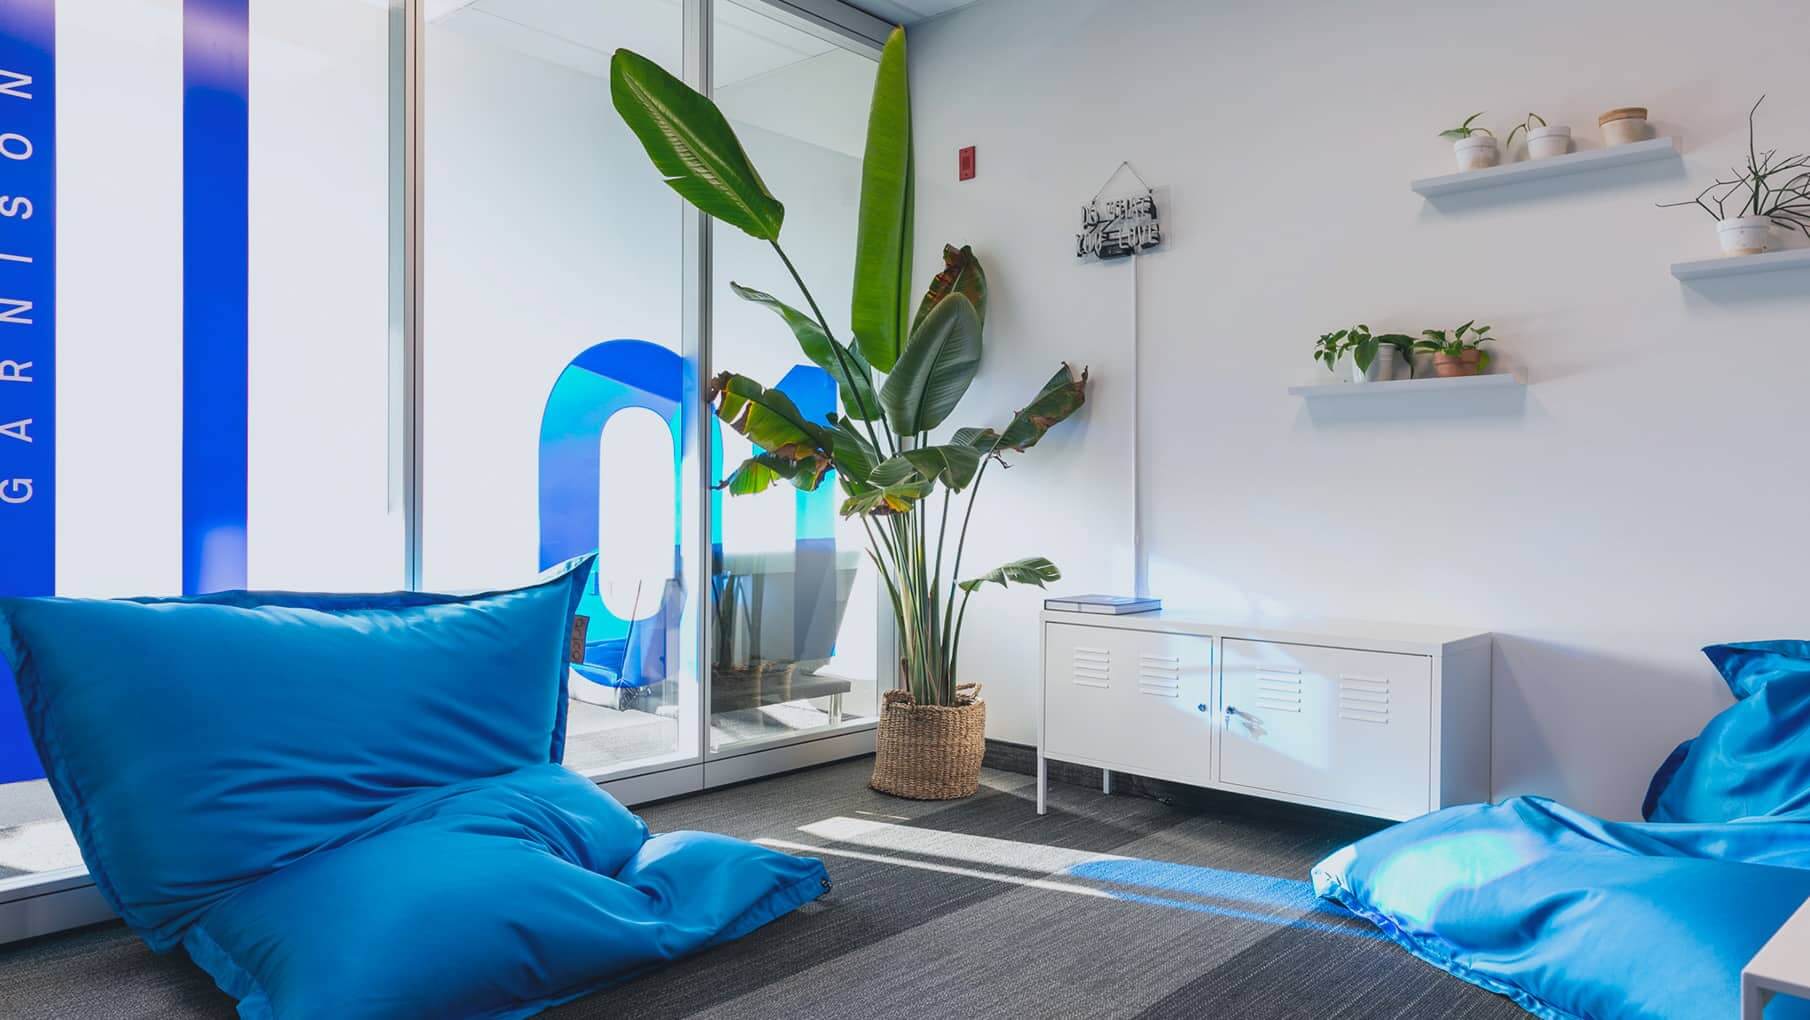
Without a doubt our most popular meeting room, thanks to our comfortable bean bags!
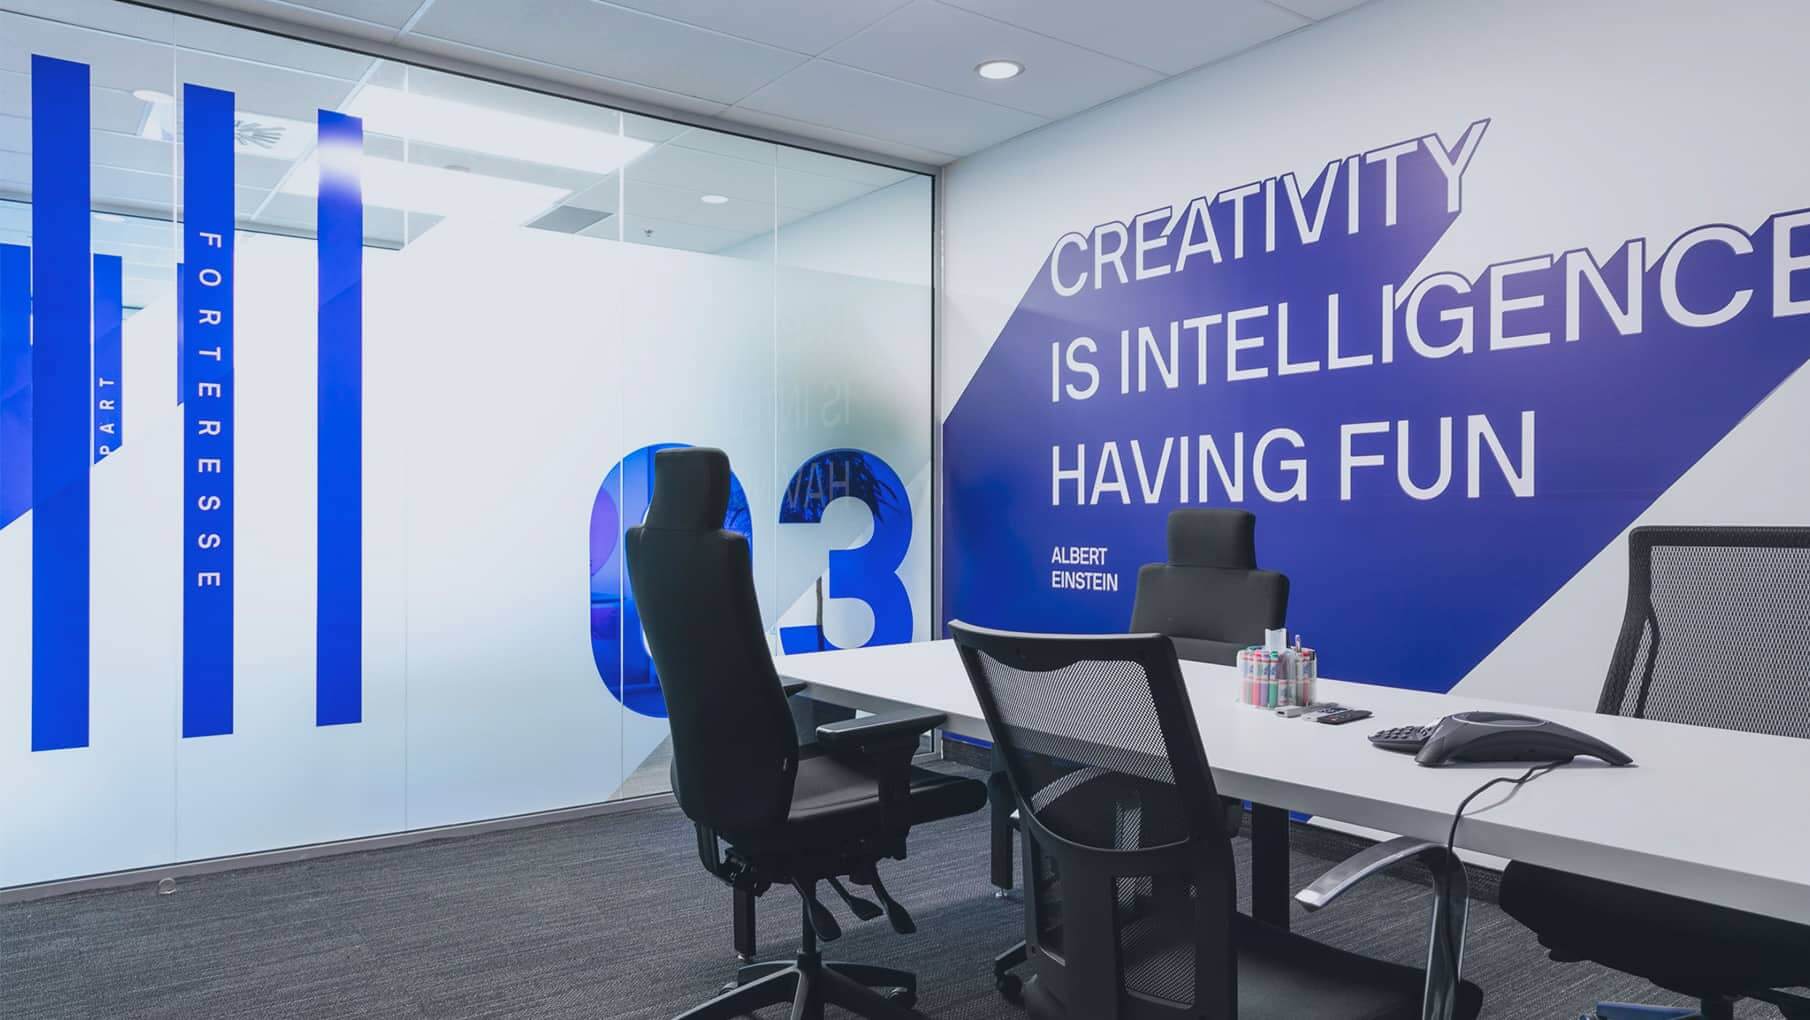
Our Quebec office has 3 conference rooms and each of them has a completely different décor!
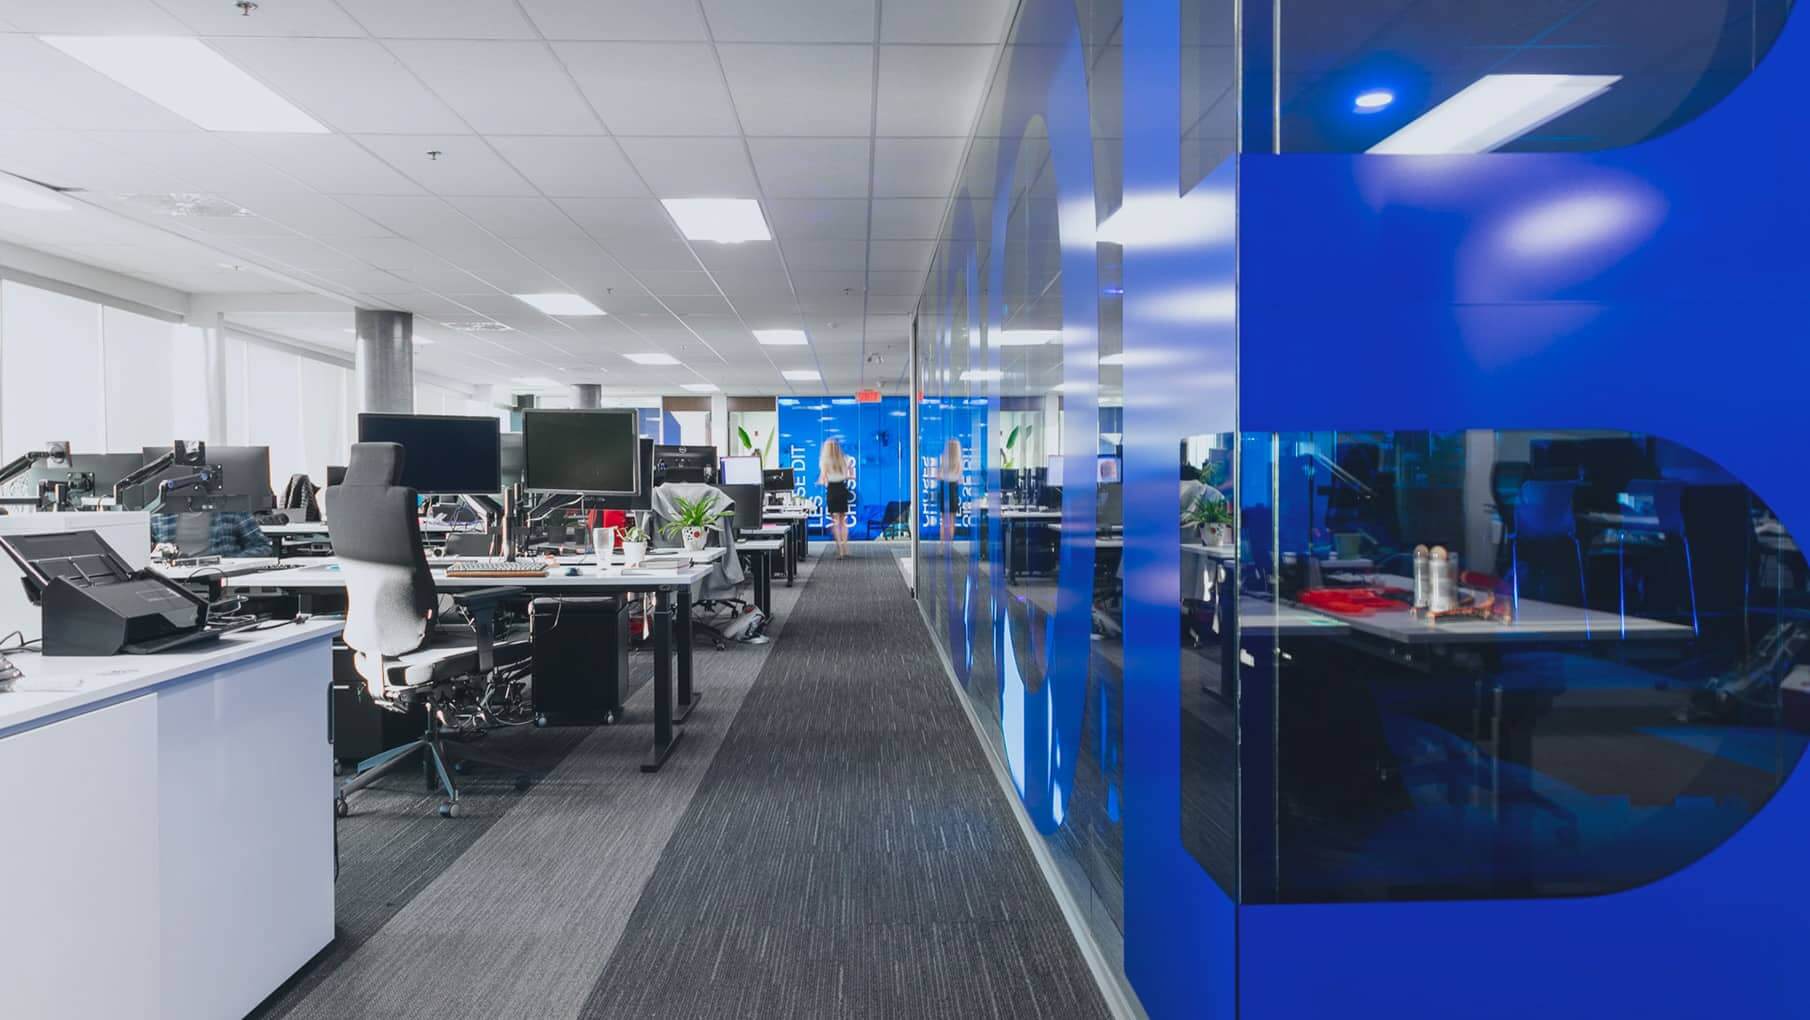
An open-plan office, fully renovated over the last year.
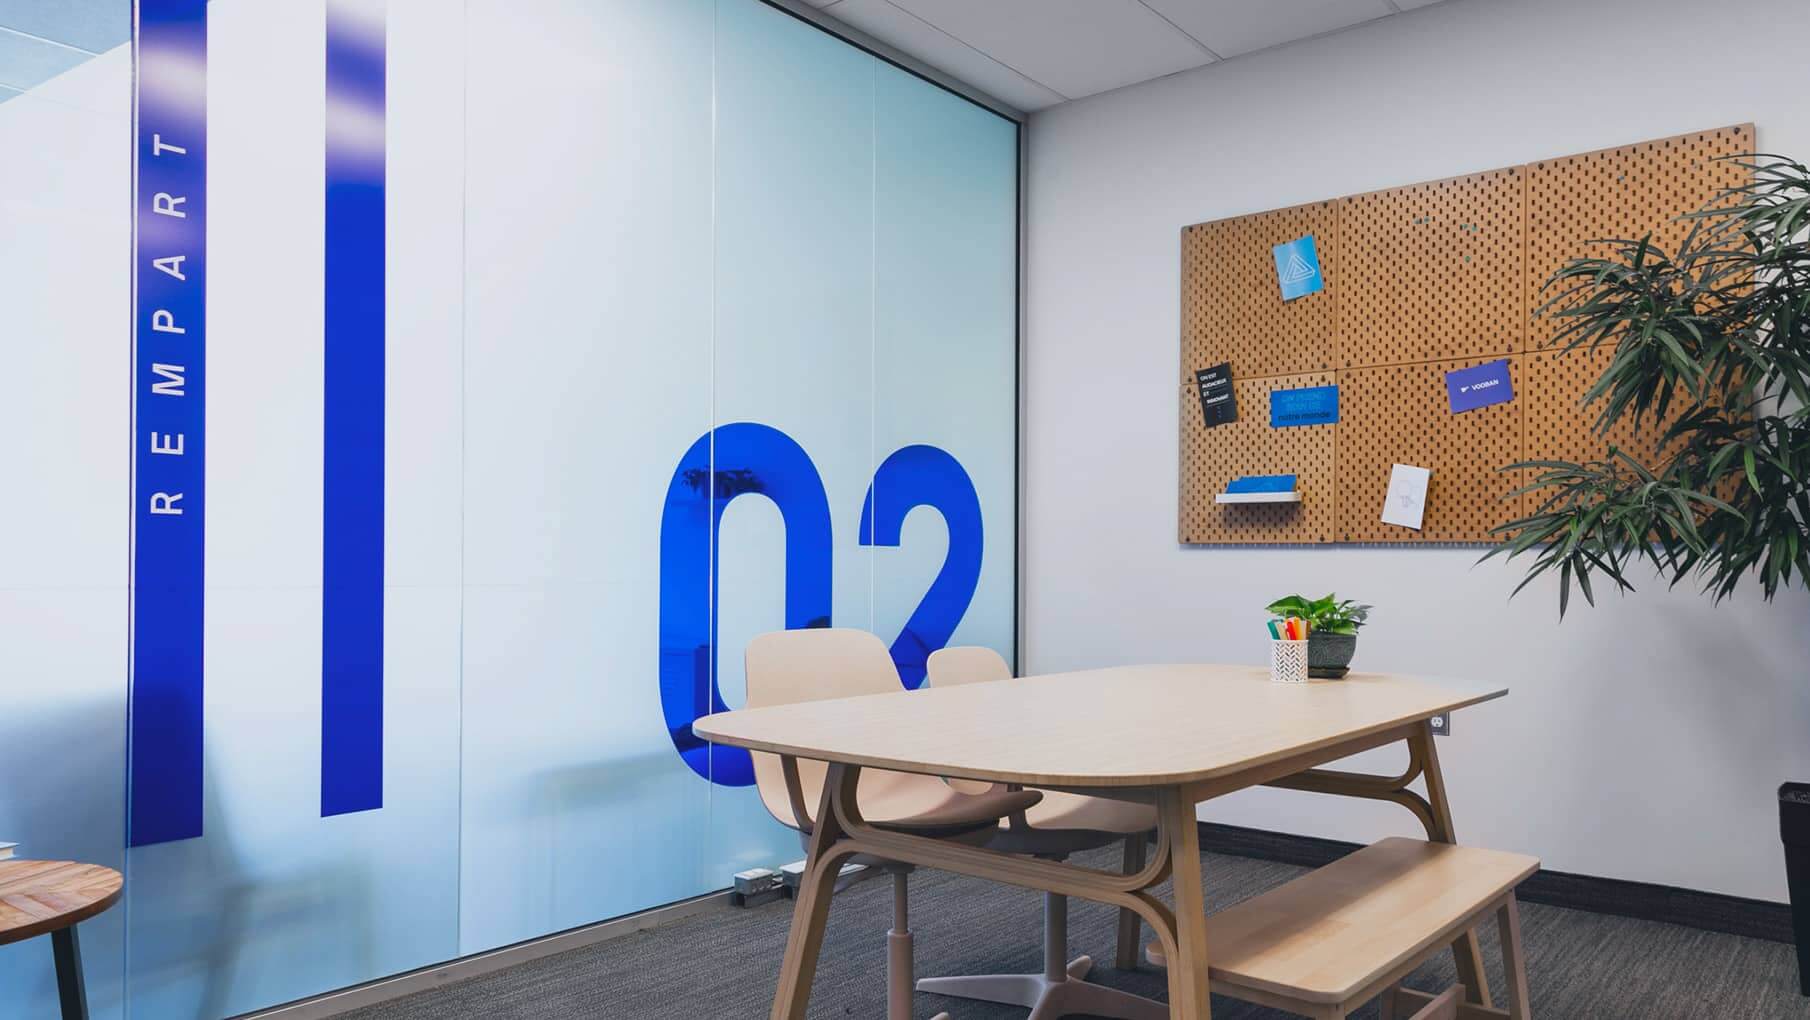
The perfect room for all your Google Meets.